The none attack tricks a backend into accepting a JWT with no signature check. If the backend trusts the token’s alg: none header, an attacker can edit the payload and claim admin rights. section 11.3.2
A forged admin token
An attacker changes the header to { "alg": "none", "typ": "JWT" }, edits the payload to { "user": "attacker", "role": "admin" }, and removes the signature. A misconfigured backend may accept it. section 11.3.2
Reduce the risk by enforcing JWT checks:
- Pin the JWT library to the expected algorithm, such as RS256. section 11.3.2
- Verify signatures using public keys fetched from the identity provider’s JWKS endpoint, and check token expiry. section 11.3.2
Figure 11.4 How a backend logic error allows forged tokens via the "none" algorithm, mitigated by explicitly pinning the verification algorithm to RS256.
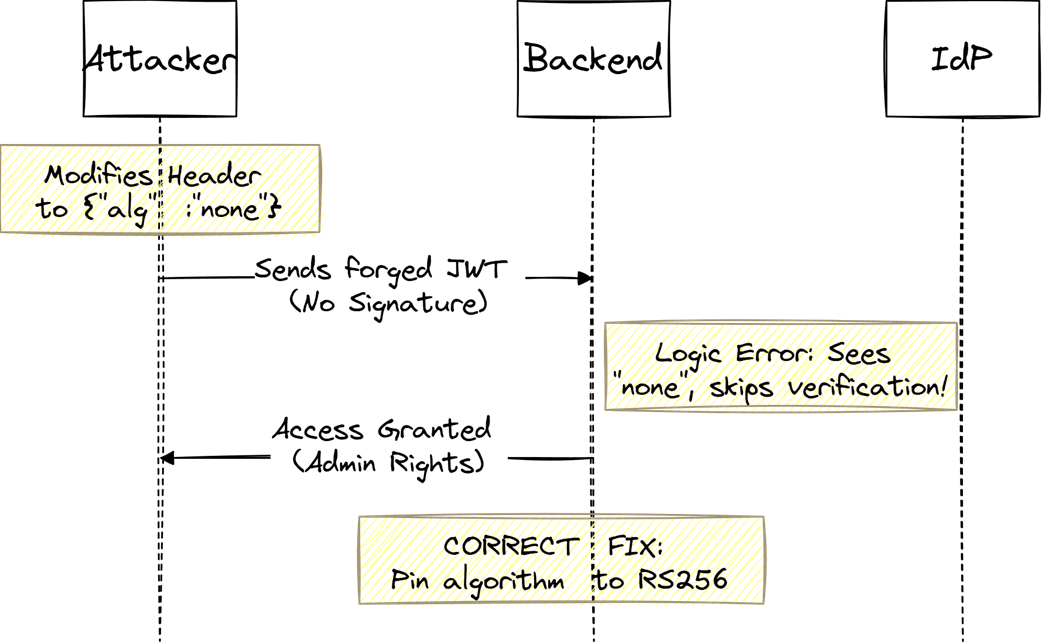
See how explicitly pinning the verification algorithm prevents the forged-token path. section 11.3.2
