The OAuth 2.0 device authorization grant lets a terminal or constrained-input device obtain authorization through a separate browser-capable device. A user authenticates with an identity provider, grants device access, and receives credentials for programmatic platform access. section 7.3.2
A typical platform flow uses GitHub for user authentication and an identity provider such as Auth0 as the secure intermediary. The provider can exchange the resulting access token for team membership, place that claim in a verifiable JWT, and include a refresh token. section 7.3.2
Platform CLI access
A CLI such as epectl directs the user to authenticate in a browser while the terminal handles the surrounding device-authorization flow. After authorization, the CLI uses the resulting short-lived credentials to access resources belonging to the user’s team. section 7.3.2 section 7.5
Figure 7.9 In this authentication and authorization flow, the IDP acts just as a secure go-between. The user must authenticate through GitHub and grant their device authorization to receive a JSON Web Token.
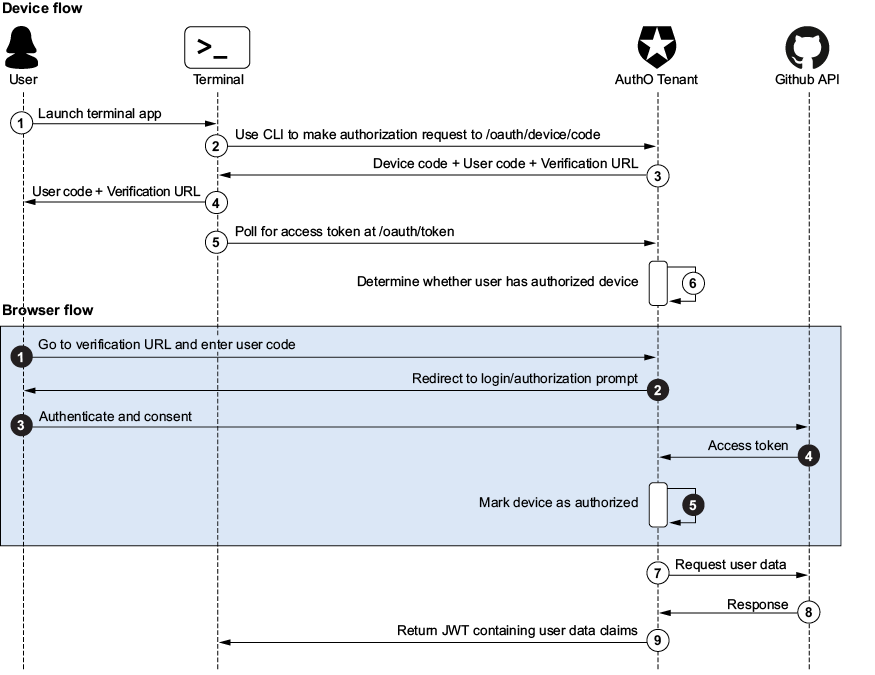
Trace the identity provider’s role as a secure go-between and follow the transition from GitHub authentication to device authorization and JWT issuance. section 7.3.2
