An OpenAPI security field records which API operations require authentication or authorization. The top-level field applies a requirement across the API; an operation-level field can override it for one HTTP operation. section 8.1
Protect most endpoints, leave one public
A ride-sharing API can declare JWTBearer under a global security field. The /protected-hello operation then inherits that requirement, while /hello sets security: [] to remain anonymous. The security scheme itself belongs under components.securitySchemes. section 8.1
Figure 8.1 We define the security schemes that protect our API in the specification’s components section under securitySchemes, and we apply them globally to the API under the specification’s security field or per operation using the operation’s security field.
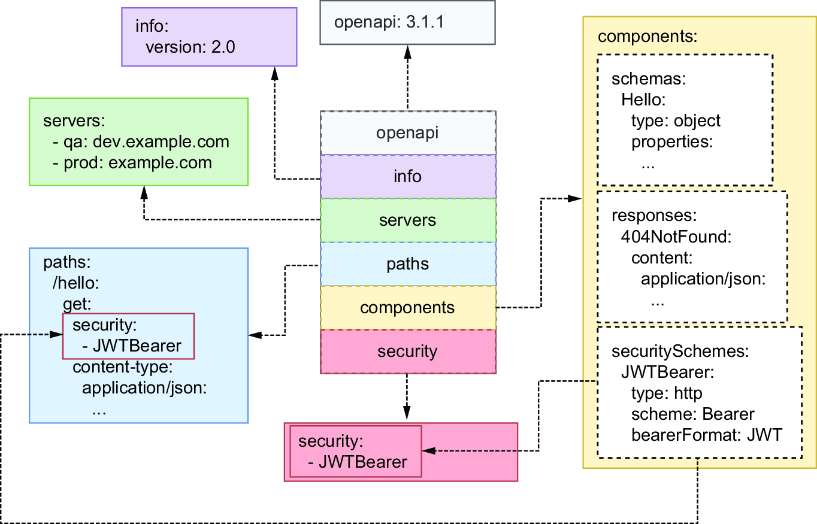
Use the figure to trace the relationship between securitySchemes definitions and global or per-operation security fields. section 8.1
Check the design before implementing it:
- Decide which operations need protection and whether user groups require different access. section 8.1
- Validate access tokens on every request and enforce operation permissions in server middleware. section 8.7
