Origin binding associates a hardware-key authentication operation with the website where the key was registered. The key signs requests for that domain, but refuses an identical-looking phishing site, so attackers cannot reuse the credential there. section 15.2
Real site versus phishing site
A key registered with https://securebank.com signs authentication requests for securebank.com. If https://fakebank.com presents a matching login page, the key will not sign its request. Verification also checks the challenge and origin before accepting authentication. section 15.2 section 15.4
Figure 15.3 The authentication process using a hardware key. The app generates a random value and asks the key to sign it with its private key. The app verifies the signature using its public key. The public key from the pair must already be configured at the app level. This configuration happens during the registration step.
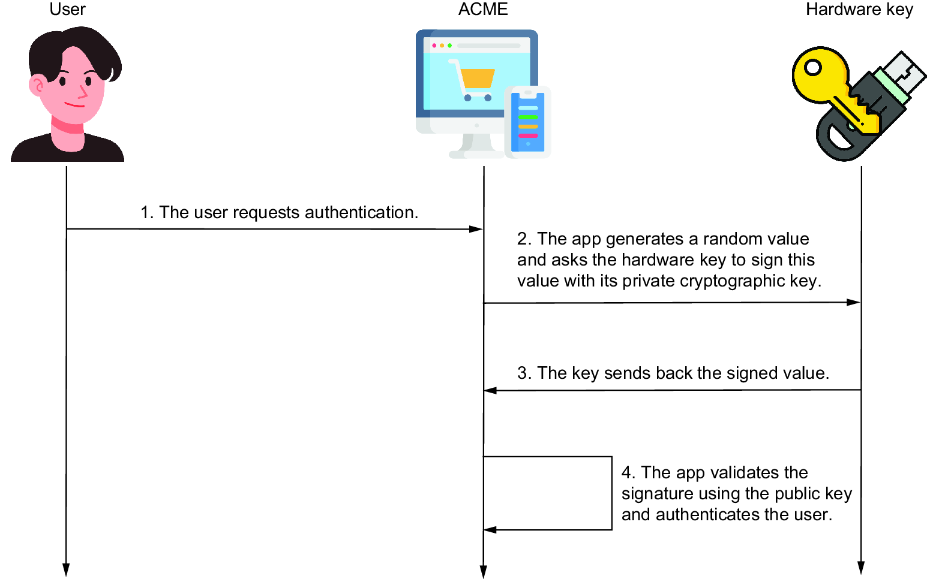
Follow the challenge-response flow from server-generated challenge through private-key signing and public-key verification. section 15.2
