liveBook · Manning

Password hashing

As explained in ASP.NET Core in Action, 3e

A password hash is a one-way derived value stored instead of the plaintext password for later password verification.

Password hashing stores a derived value instead of the plaintext password, so an application can retain user credentials without keeping the original password. Use a strong hashing algorithm and let an established identity system handle the security-sensitive details. section 29.5 section 23.2

ASP.NET Core Identity includes password hashing alongside user storage, password validation, account lockout, multifactor authentication, and password-reset support. This avoids manually building an authentication and membership system while leaving the login UI and some integrations to the application. section 23.1.2 section 23.2

Practical guidance:

  • Store passwords only as hashes; do not retain plaintext passwords. section 29.5
  • Prefer ASP.NET Core Identity or an external identity provider instead of writing password and membership handling manually. section 23.1.2 section 23.2
  • Combine password hashing with password protection against weak or compromised passwords and with MFA where possible. section 29.5 section 23.2
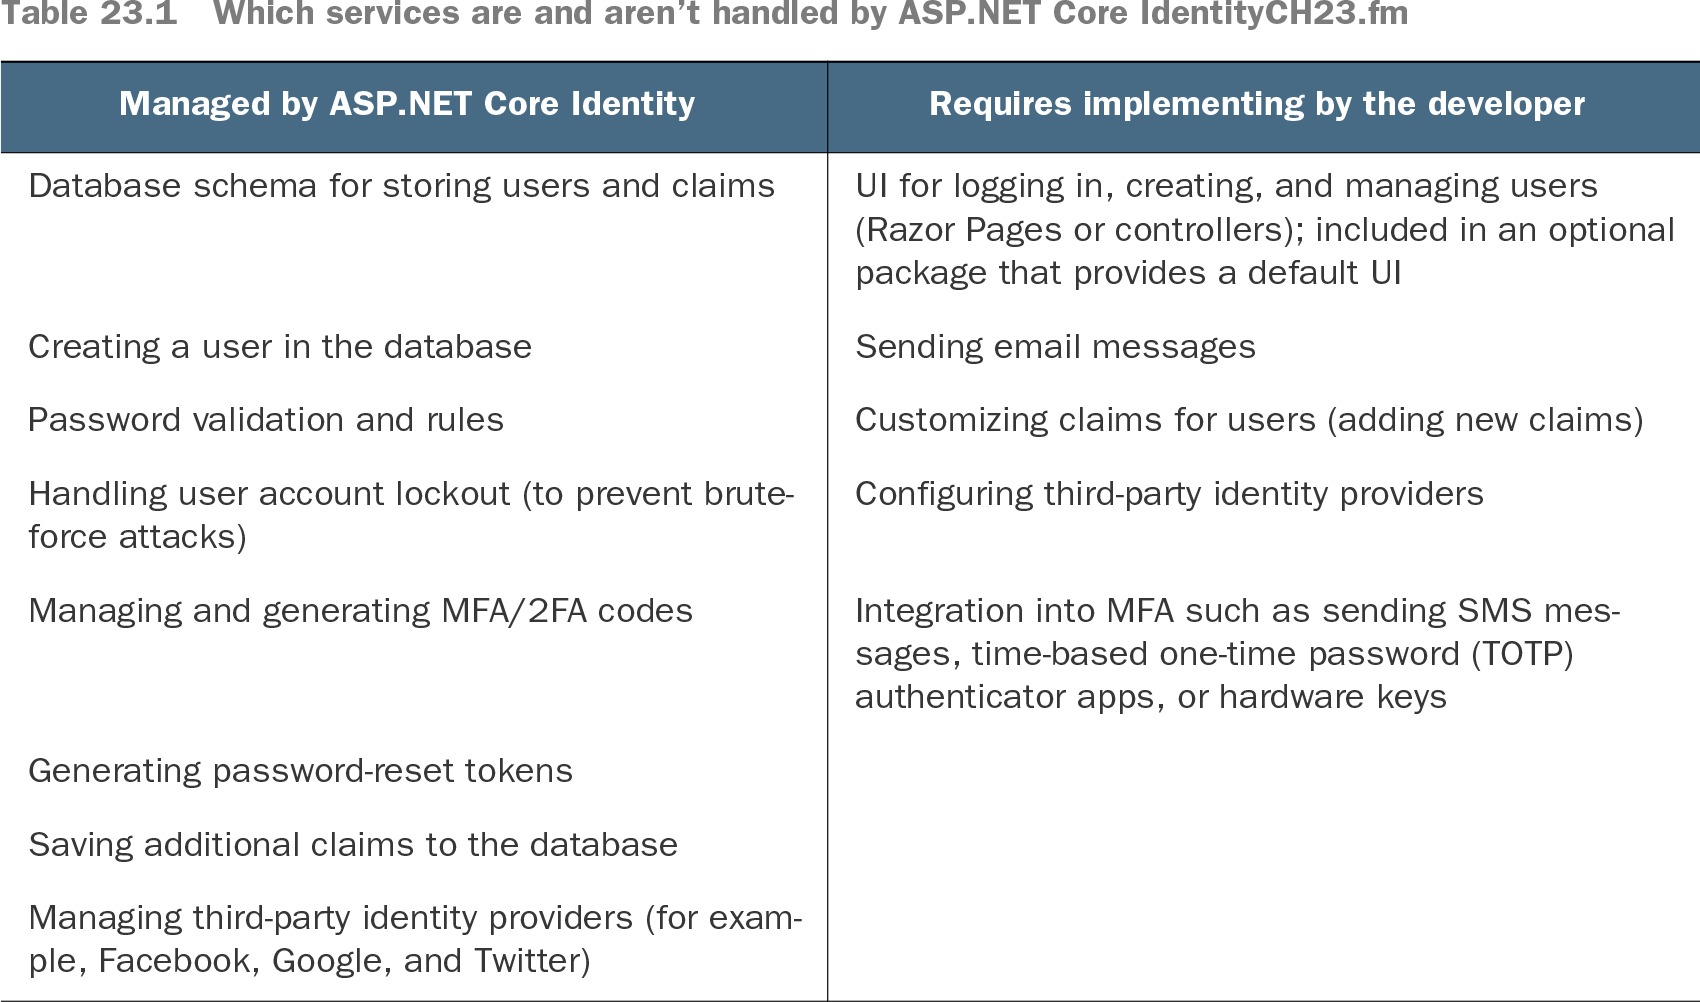
Table 23.1 Which services are and aren’t handled by ASP.NET Core IdentityCH23.fm (view table figure)

Managed by ASP.NET Core Identity

Requires implementing by the developer

Database schema for storing users and claims

UI for logging in, creating, and managing users (Razor Pages or controllers); included in an optional package that provides a default UI

Creating a user in the database

Sending email messages

Password validation and rules

Customizing claims for users (adding new claims)

Handling user account lockout (to prevent brute-force attacks)

Configuring third-party identity providers

Managing and generating MFA/2FA codes

Integration into MFA such as sending SMS messages, time-based one-time password (TOTP) authenticator apps, or hardware keys

Generating password-reset tokens


Saving additional claims to the database


Managing third-party identity providers (for example, Facebook, Google, and Twitter)


Use the responsibility table to distinguish password hashing and validation, which Identity manages, from login UI and external messaging, which the application may need to provide. section 23.2


How ASP.NET Core in Action, 3e covers it

How deep it goes
Recommends hash-only storage and strong algorithms but does not explain hashing internals or algorithm selection.
Examples
Uses ASP.NET Core Identity storing users in a database and applying a strong hashing algorithm as the practical example.
What it assumes
Assumes basic user authentication and database needs while recommending Identity to supply the security-sensitive implementation.
What you can do after
Operate/configure ASP.NET Core Identity to store passwords as hashes instead of implementing credential handling manually.
How it connects
Connects password hashing with ASP.NET Core Identity, password validation, multifactor authentication, account lockout, and brute-force protection.

Also explained in

Compare how 5 books explain password hashing →

Related concepts

This explainer was generated by Manning's knowledge graph from the text of ASP.NET Core in Action, 3e. The section links point to the parts of the book it draws on.