PKCS#11 is a standard API for accessing cryptographic tokens and performing protected key and cryptographic operations. HSMs commonly implement it so different systems can interoperate. section 13.2.3 section 13.5
PKCS#11 appears wherever sensitive operations need hardware protection:
- Verifying ATM PINs through an HSM. section 13.2.3
- Protecting a certificate authority’s private key and possibly terminating TLS connections. section 13.2.3
- Protecting encrypted phone backups while keeping the cloud provider from accessing their keys. section 13.2.3
Its long history creates tradeoffs. PKCS#11 v2.40, released in 2015, retains older algorithms and practices that can introduce vulnerabilities; v3.0, released in 2020, adds Curve25519, EdDSA, and SHAKE. The interface helps systems interoperate, but it does not guarantee that an HSM is secure: software bugs and side-channel attacks can still expose operations or keys. section 13.2.3 section 13.5
Figure 13.2 An IBM 4767 HSM as a PCI card. Photo from Wikipedia (http://mng.bz/XrAG).
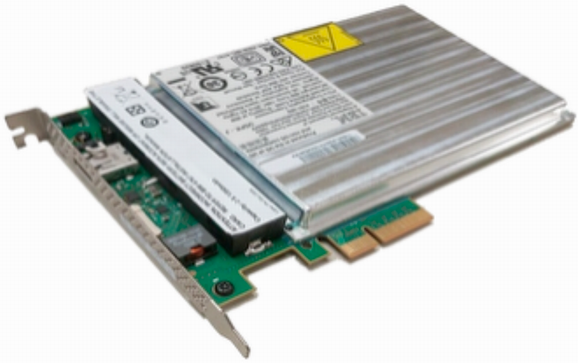
An HSM shown as a PCI card makes the hardware endpoint behind a PKCS#11 interface concrete. section 13.2.3
