Podman auto-update detects a changed container image in a registry, pulls it, and recreates the associated container without manual intervention. It suits distributed, edge, and IoT workloads where images may contain new features or vulnerability fixes. section 7.3.4
Enable updates by creating the container with the io.containers.autoupdate=registry label and generating its systemd unit with podman generate systemd --new. Reload and start the unit, then run podman auto-update to check the registry. section 7.3.4
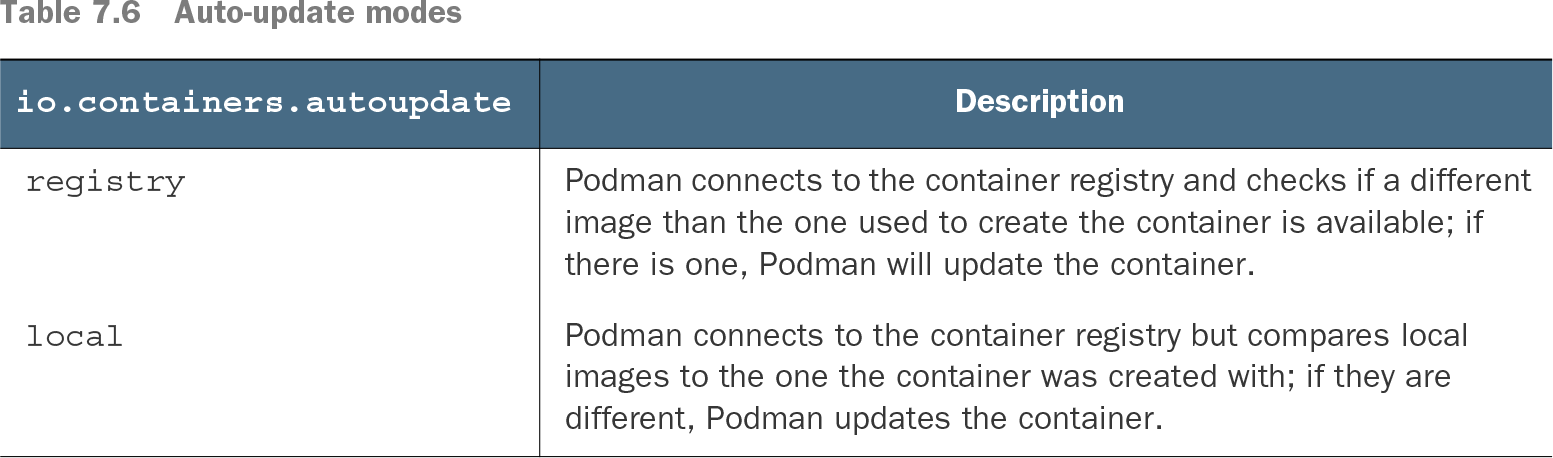
Table 7.6 Auto-update modes (view table figure)
Compare registry and local update policies: registry compares against the image available in the container registry, while local compares registry state with local images. section 7.3.4
Reliable rollback depends on systemd notification. A containerized service receives NOTIFY_SOCKET through the unit; if it fails to report readiness within the limit, Podman removes the replacement, restores the original image, and recreates the previous container. section 7.4 section 7.5