A port security violation occurs when a frame arrives from a MAC address that exceeds the port’s permitted secure-MAC limit. With the default maximum of one address, a second unique MAC address triggers the violation, commonly during a MAC flooding attack. section 12.1.2 section 12.3
Track the violation through these operational effects:
- The default violation action is shutdown, which error-disables the port. section 12.1.2 section 12.3
- Dynamically learned secure MAC addresses are forgotten when the port is disabled, while the triggering address remains in Last Source Address:Vlan. section 12.1.2
- Security Violation Count increments each time Port Security disables the port. section 12.1.2
- Port Security limits MAC addresses but does not inherently distinguish spoofed frames from legitimate devices. section 12.1.2
Diagnosing and recovering F0/1
After F0/1 allows one learned MAC address, a frame from 00e0.4c68.92ff causes a security violation. Use show port-security interface f0/1 to find Secure-shutdown, Total MAC Addresses 0, the triggering Last Source Address, and Security Violation Count 1. Manually recover the port with shutdown followed by no shutdown. Automatic recovery is disabled by default; enable it with errdisable recovery cause psecure-violation.
Figure 12.2 Using Port Security, SW1 error-disables F0/1 when it detects more than one unique MAC address on the port, preventing a MAC flooding attack.
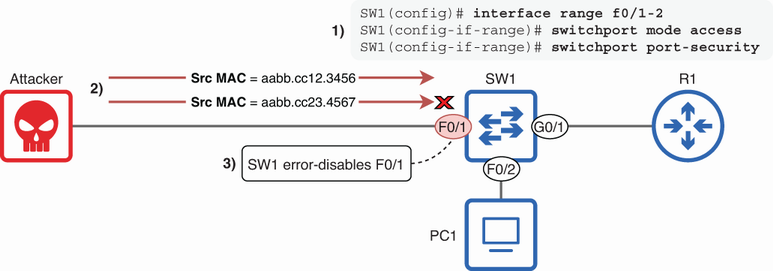
Visualizes how exceeding the unique-MAC limit error-disables the port and prevents a MAC flooding attack. section 12.1.2
