A preflight request is a browser-generated HTTP OPTIONS request that tests whether a cross-origin request is permitted before the browser sends the original request. The browser owns this decision; application code does not implement the preflight logic. section 10.1
A preflight flow proceeds as follows:
- The browser sends an OPTIONS request when the cross-origin request requires preflight. section 10.1
- The server responds with CORS headers describing allowed origins and methods. section 18.7
- If the preflight fails, the browser does not honor the original request; if it succeeds, the browser sends it. section 10.1
Testing a preflight response
A MockMvc test can perform OPTIONS on /test with Origin and Access-Control-Request-Method: POST, then verify Access-Control-Allow-Origin, Access-Control-Allow-Methods, and a successful status. section 18.7
Figure 10.4 For simple requests, the browser sends the original request directly to the server. The browser rejects the response if the server doesn’t allow the origin. In some cases, the browser sends a preflight request to test whether the server accepts the origin. If the preflight request succeeds, the browser sends the original request.
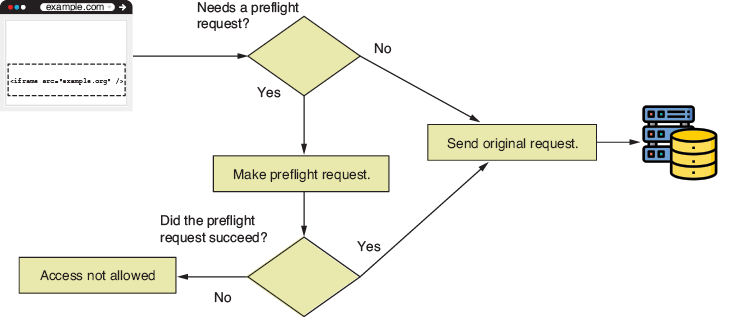
Shows the contrast between direct simple requests and requests preceded by a preflight check. section 10.1


