A proof statement is the public claim and public inputs whose correct relationship a cryptographic proof establishes. In a SNARK-style QAP, it is separated from the private witness. section 19.2
A proof statement has three practical roles:
- Publishes the values that define the claim while keeping witness values private. section 19.2
- Orders public variables first so their indexes match the common reference string (CRS). section 19.5.4
- Travels with proof points A, B, and C in the generated record. section 19.5.4
The QAP represents the claimed computation with wires and multiplication gates. Its wire values satisfy an identity involving vj(x), wj(x), yj(x), and h(x)t(x); the statement supplies selected wire values, while the witness supplies the remaining values. section 19.2 section 19.5.4
Medical-record statement
A medicine number and dose are public statement values; the patient number remains in the witness. Derived wires affected by those public values are also public, while a random intermediate wire prevents backward recovery of the patient number. section 19.5.4 section 19.2
Figure 19.2 Example quadratic arithmetic program
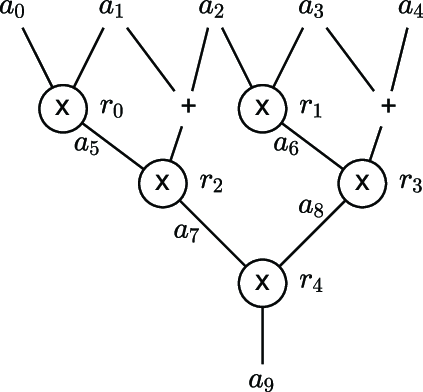
Use the QAP diagram to trace which wires become public statement values and which remain witness-dependent. section 19.2
