A public key set is a collection of public cryptographic keys that a resource server retrieves from an authorization server to verify JWT access-token signatures. The authorization server keeps the corresponding private keys for signing tokens. section 15.1
Figure 15.2 The resource server retrieves a set of public keys from the authorization server through an endpoint made available by the authorization server. The resource server then uses these keys to verify the signature of the access token.
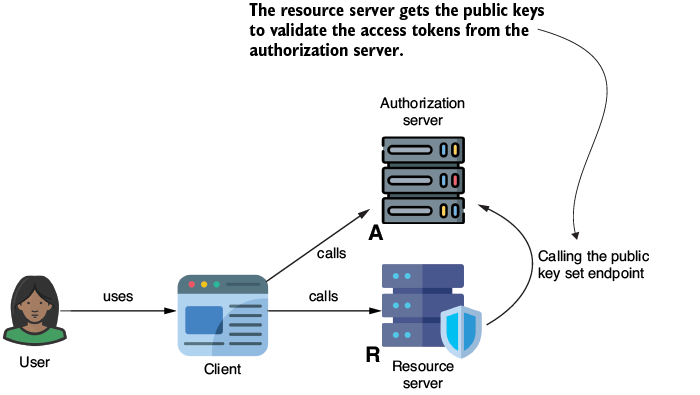
The resource server obtains the key set through an authorization-server endpoint, then uses the keys to verify access-token signatures. section 15.1
Configure a Spring resource server
Expose the authorization server's jwks_uri, such as http://localhost:8080/oauth2/jwks, as a property and configure Spring Security with oauth2ResourceServer().jwt().jwkSetUri(keySetUri). Add authorization rules so requests require authentication, then test a protected endpoint with a bearer token. section 15.1
