Queryable Encryption lets a MongoDB application search sensitive encrypted fields without revealing their plaintext to the database service. An equality match on a Social Security number is one example. The application encrypts data before it reaches Atlas and decrypts returned data on the client. section 20.5.4 section 20.8
An encrypted query follows this path:
- An authenticated client submits a query targeting an encrypted field. The MongoDB driver identifies the field and obtains keys from a customer-provisioned key provider. section 20.5.4
- The driver encrypts the query; MongoDB processes it without decrypting it and returns encrypted results. section 20.5.4
- The driver decrypts the results for the client. Keep decryption keys accessible to the application, not Atlas. section 20.5.4
Figure 20.3 An authenticated client (1) submits a query containing sensitive information, such as a Social Security number (SSN). The MongoDB driver (2) analyzes the query and identifies that it targets an encrypted field, prompting a request for encryption keys from a customer-provisioned key provider. Using these keys (3), the driver encrypts the query and sends it to MongoDB Server (4), where it is processed without decryption, ensuring that sensitive data remains secure and hidden. The server returns encrypted results (5) to the driver, which decrypts them and provides the plain-text data to the client (6), maintaining end-to-end security throughout the process. (Image © MongoDB 2024 CC BY-NC-SA 3.0)
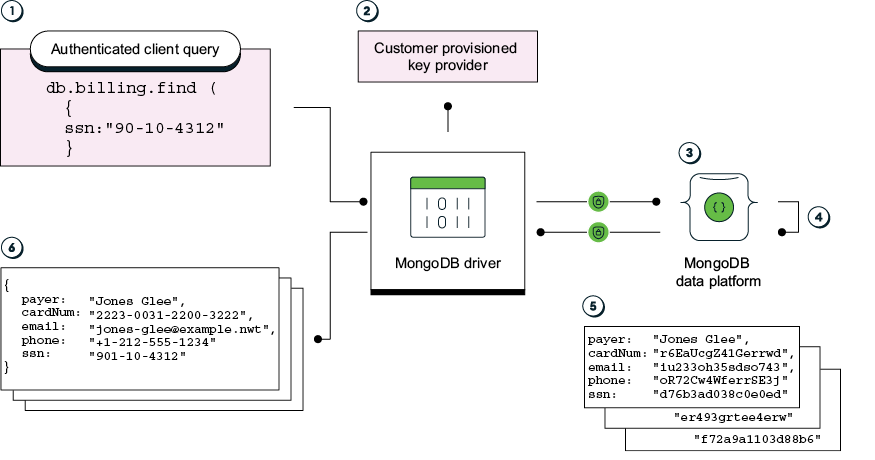
The diagram traces the query from the authenticated client through driver-side encryption, server-side processing, and client-side decryption. section 20.5.4
Use Queryable Encryption when fields must remain hidden from Atlas but still need to be searched. It complements other defenses rather than replacing them: use authentication and role-based access control to restrict access, and auditing to monitor operations. Client-side field-level encryption also protects sensitive fields before storage; Queryable Encryption addresses the additional need to query encrypted fields. section 20.7 section 20.8
