A random number is a value selected through a process intended to resist prediction. In cryptography, unpredictability matters because keys, passwords, and other secrets become easier to guess when outputs favor some values over others. section 2.0 section 2.1
Treat cryptographic random numbers as requiring both unpredictability and a uniform distribution:
- Prefer outputs evenly distributed across the full range of possible values; even slight bias can reduce the attacker’s search space. section 2.1 section 2.1.1
- Use randomness when generating secret keys, mixing passwords with stored values, or preventing identical encrypted election ballots from revealing the same vote. section 2.1.1
- Treat ordinary linear-congruential generators as learning and exploitation exercises, not as suitable generators for security-sensitive applications. section 2.0
Biased date passwords
An eight-digit password formed from MMDDYYYY appears to offer 100 million possibilities, but restricting it to valid dates leaves only 55,800 combinations. Bias therefore makes guessing substantially easier. section 2.1.1
Figure 2.1 RNGs generate random numbers that are hard to predict.
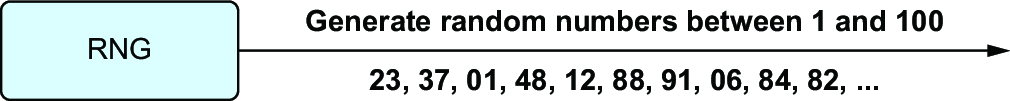
Visualizes a random-number generator as producing an arbitrary sequence whose outputs are hard to predict. section 2.0



