liveBook · Manning

Resource server

As explained in Acing the CCNA Exam: Volume 2 Advanced Networking and Security

A resource server is a service that hosts protected resources and validates access tokens before providing them to authorized clients.

A resource server hosts protected API resources and grants access when a client presents a valid access token. In bearer authentication, the client obtains the token from an authorization server and sends it to the resource server instead of repeatedly transmitting credentials. section 23.3.2

The operational relationship is:

  • The client obtains an access token from the authorization server. section 23.3.2
  • The client presents the token when requesting the desired API resource. section 23.3.2
  • The resource server uses the token to authorize access to its protected resources; HTTPS protects the token in transit. section 23.3.2
  • A single server can sometimes perform both authorization-server and resource-server roles. section 23.3.2

Bearer-authentication flow

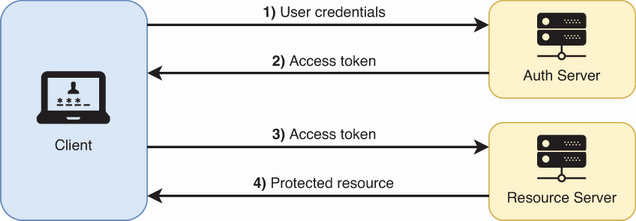
A client requests an access token, then uses that token to access an API hosted by the resource server. Intercepting the token could provide unauthorized access, so the exchange requires HTTPS. section 23.3.2

Figure 23.6 REST API bearer authentication. A client obtains an access token from an authorization token and uses the token to access the desired resource on the resource server.
A close-up of a list of access Description automatically generated

Shows the client, authorization server, access token, and resource server in one bearer-authentication flow. section 23.3.2


How Acing the CCNA Exam: Volume 2 Advanced Networking and Security covers it

How deep it goes
Defines the bearer and OAuth 2.0 flow, but stops short of implementation commands and token-validation internals.
Examples
Uses a REST API bearer-authentication diagram showing token issuance followed by access to a desired resource.
What it assumes
Assumes clients, access tokens, authorization servers, and protected resources as the basic vocabulary.
What you can do after
Evaluate how bearer authentication and OAuth 2.0 separate token issuance from protected-resource access.
How it connects
Connects clients, authorization servers, access tokens, bearer authentication, OAuth 2.0, and protected resources.

Also explained in

Compare how 4 books explain resource server →

Related concepts

This explainer was generated by Manning's knowledge graph from the text of Acing the CCNA Exam: Volume 2 Advanced Networking and Security. The section links point to the parts of the book it draws on.

