A policy reviewer is an engineer who examines an authorization policy implementation through the standard code review process. The reviewer checks whether the implementation matches the intended access behavior and preserves required accountability. Separation of duties requires the reviewer to be different from the policy author. section 14.3.2
A reviewer contributes to policy governance by:
- Evaluating policy logic before deployment as part of the normal engineering review workflow. section 14.3.2 section 14.6
- Checking that the implementation remains consistent with shared policy standards, templates, metadata, and review processes. section 14.3.1
- Providing an independent checkpoint alongside the owner, author, approver, coordinator, and auditor. section 14.3.2
- Helping create an evidence trail through review records, decision documentation, and links to operational follow-up. section 14.3.1 section 14.6
Independent policy review
Alice authors an authorization policy and records its rationale. Bob, a different engineer, reviews the implementation. Carol approves the intended business rule and scope, while a coordinator checks alignment with shared standards. This arrangement keeps technical review independent without moving every decision to a central authority. section 14.3.2 section 14.3.1
Figure 14.5 Policy governance workflow across roles. Authorization policies move through clearly defined roles, from creation to deployment and review. Engineers author and review policy logic, managers approve intent and scope, access control coordinators ensure alignment across teams, and auditors verify that governance processes are followed over time. Separation of duties and feedback loops preserve accountability without centralizing control.
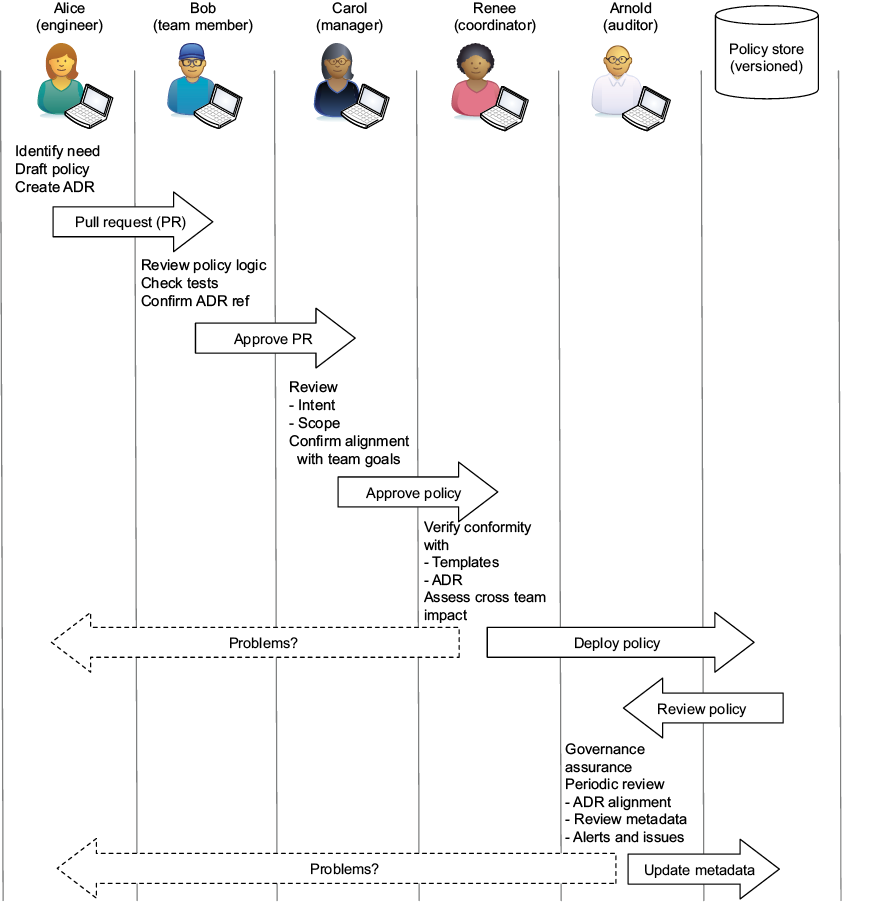
Use the governance workflow to trace how independent review connects policy creation, approval, coordination, deployment, and continuing oversight. section 14.3.2


