liveBook · Manning

Ring-based deployment strategy

As explained in GitHub Actions in Action: Continuous integration and delivery for DevOps

A ring-based deployment strategy releases software progressively to successive groups of users or environments called rings.

A ring-based deployment strategy releases software progressively to successive groups of users or production environments. Each ring has an acceptable risk level; telemetry and incident checks determine whether exposure can advance. section 9.3.8

A practical ring-based workflow combines staged environments with controlled exposure:

  • Deploy the software to a first ring containing a small, risk-tolerant user group, often through a canary release. section 9.3.8
  • Route users to the ring through domain prefixes, traffic management, percentage-based routing, headers, or query-string variations. section 9.3.8 section 9.3.5
  • Monitor telemetry and live-site incidents, then approve progression only when the application behaves as expected. section 9.3.8
  • Roll back by disabling a feature toggle or routing traffic back to the known working version when anomalies appear. section 9.3.8 section 9.3.5

Environment-based progression

A delivery pipeline can retrieve deployment artifacts, deploy to internal staging, run Playwright end-to-end checks, and then promote the application through production rings using manual or automated approvals. section 9.1.1

Figure 9.6 Ring-based deployment
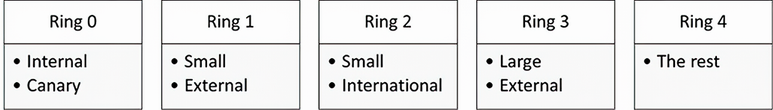
Use the deployment progression diagram to relate rings, staged exposure, monitoring, and promotion decisions. section 9.3.8

How GitHub Actions in Action: Continuous integration and delivery for DevOps covers it

How deep it goes
Explains ring selection, canary exposure, routing, telemetry gates, and rollback, but leaves routing implementation application-specific.
Examples
Uses domain-prefixed rings, percentage routing, Playwright checks, staging environments, and manual or automated approvals.
What it assumes
Assumes deployable production environments, user or traffic segmentation, telemetry, and health validation; staging and approvals are explicitly introduced.
What you can do after
Operate/configure staged releases that limit exposure, validate production behavior, and support rapid rollback.
How it connects
Connects canary releases, feature toggles, traffic routing, telemetry, deployment environments, and continuous delivery.

Related concepts

This explainer was generated by Manning's knowledge graph from the text of GitHub Actions in Action: Continuous integration and delivery for DevOps. The section links point to the parts of the book it draws on.