A satisfied policy is a policy whose conditions match the context of an authorization request. Matching makes it eligible for evaluation, but does not guarantee that it determines the final allow or deny decision. section 4.3.2
Distinguish two related sets:
- Satisfied policies match the request context and may influence evaluation. section 4.3.2
- Determining policies are the satisfied policies that directly cause the authorization response, making them a subset of the satisfied set. section 4.3.2
Context changes without role changes
A user may temporarily lose permission to merge records or update ticket status even though their roles remain unchanged; when the relevant context changes tomorrow at 9 a.m., those entitlements are restored. section 4.3.2
Figure 4.1 Relationships among key authorization terms. Principals, actions, and resources form the core of access decisions and are enriched with attributes, roles, and group memberships. All entities exist within namespaces and can be either principals or resources. The diagram also shows the legacy term subject as an older equivalent of principal and illustrates how actions operate on resources based on contextual and identity-based properties.
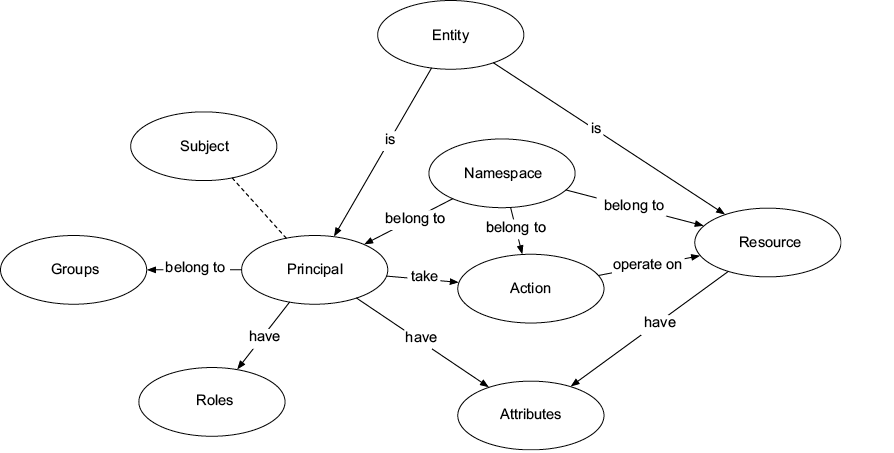
Relates policy matching to principals, actions, resources, attributes, roles, group memberships, and authorization context. section 4.3.2
