A scope-based authorization policy permits an API operation only when the bearer access token contains a required scope. The API defines what each scope means and applies the policy to protected endpoints. section 25.6
Use scopes to express API access boundaries:
- Require a recipe.edit scope on endpoints that edit recipes. section 25.6
- Require an application-wide scope such as recipeApi, which can sometimes replace audience validation. section 25.6
- Remember that scopes have no inherent behavior; the API must connect them to authorization policies. section 25.6
Recipe editing policy
Register a policy such as RecipeEditScope with RequireClaim("scope", "recipe.edit"), then apply it to the minimal API endpoints that edit recipes. section 25.6
Figure 25.12 Authorizing a request to a minimal API endpoint. The routing middleware selects an endpoint that is protected by an authorization requirement. The authentication middleware decodes and verifies the bearer token, creating a ClaimsPrincipal, which the authorization middleware uses along with the endpoint metadata to determine whether the request is authorized.
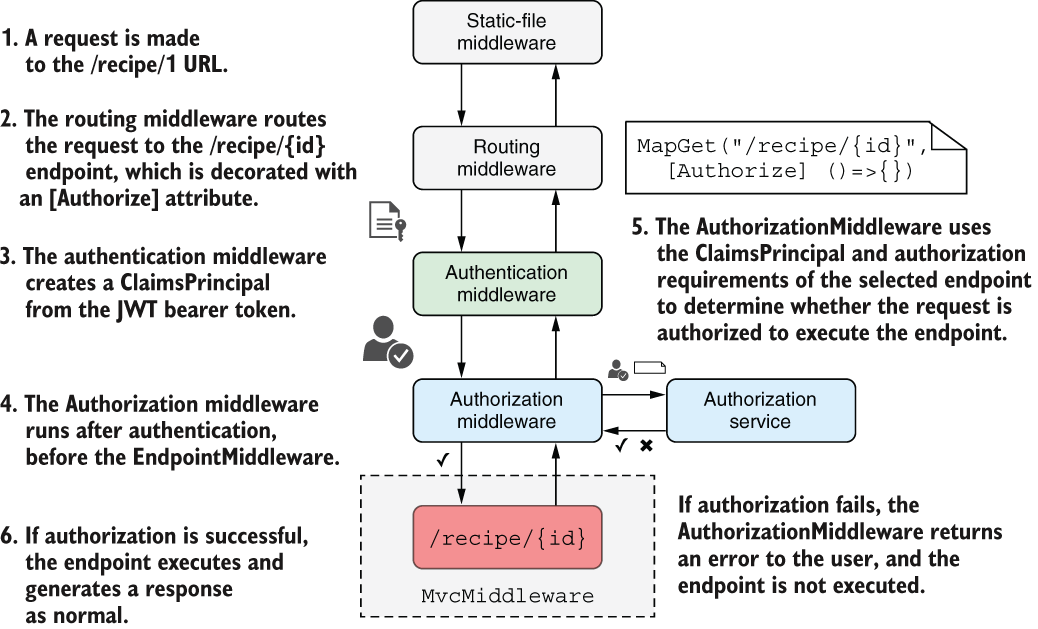
Trace how routing selects a protected endpoint, authentication verifies the bearer token and creates a ClaimsPrincipal, and authorization evaluates the endpoint requirement. section 25.6
