Secure by design incorporates security controls into the software development life cycle instead of adding them only through top-down policy enforcement. section 5.2
Product-driven organizations treat security as a peer function alongside engineering, product management, and operations. The approach emphasizes influence, partnership, and integration across teams. section 5.2
Agile product development
A technology company has security teams work directly with product and engineering leads during agile development cycles, embedding security controls in the software development life cycle. section 5.2
Figure 5.2 An example of aligning cybersecurity initiatives within the business environment and a typical reporting structure. CISOs most often report to the CIO. Also, the CISO will sometimes report directly to the board.
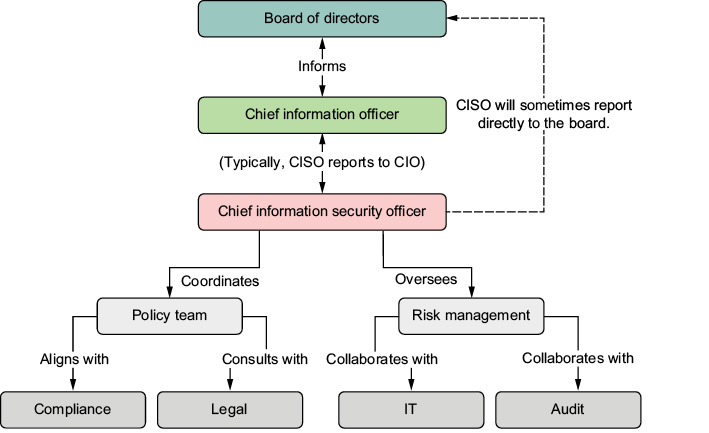
Compare hierarchical cybersecurity reporting with organizational alignment across leadership, policy, and risk management. section 5.2


