Secure multiparty collaboration lets parties jointly compute over sensitive data and proprietary models without exposing either asset to the other. A trusted execution environment (TEE) places both inside a protected enclave, even on an untrusted server. section 9.2.1
A secure multiparty compute cycle typically proceeds as follows:
- Define approved data providers and result consumers. section 9.2.1
- Upload sensitive data and the computation into the enclave. section 9.2.1
- Release results only to authorized consumers after the task completes. section 9.2.1
Hospital data and a proprietary AI model
An institution supplies its model while a hospital supplies confidential patient records. Both are loaded into an enclave, allowing training without either party exposing its sensitive asset. section 9.2.1
Figure 9.3 Secure multiparty computation using a TEE. Sensitive data and proprietary models are loaded into an enclave within an untrusted server. The computation runs securely inside the TEE, keeping both inputs confidential from the hosting environment.
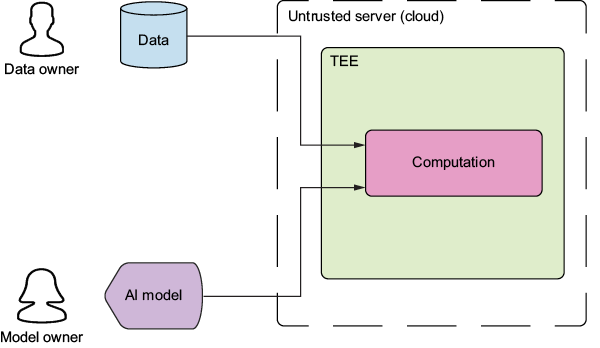
Shows sensitive data and proprietary models entering an enclave inside an untrusted server, with computation protected from the hosting environment. section 9.2.1
