A security scheme is an OpenAPI configuration object that documents how an API authenticates and authorizes requests, including token type, placement, authorization details, and access scopes. section 8.1
Apply a security scheme deliberately:
- Decide which operations require authentication and whether user groups, such as drivers and passengers, need different access. section 8.1
- Define schemes under components.securitySchemes, then apply them globally or override them for individual operations. section 8.1
- For JWTs, validate signatures, claims, and permitted algorithms on every request; middleware is the recommended location. section 8.7
JWT bearer scheme
An OpenAPI 3.1.1 specification can define a JWT bearer scheme with type http, scheme Bearer, and bearerFormat JWT. A global security requirement can protect the API, while an operation such as /hello can set security: [] to remain public. section 8.1
Figure 8.1 We define the security schemes that protect our API in the specification’s components section under securitySchemes, and we apply them globally to the API under the specification’s security field or per operation using the operation’s security field.
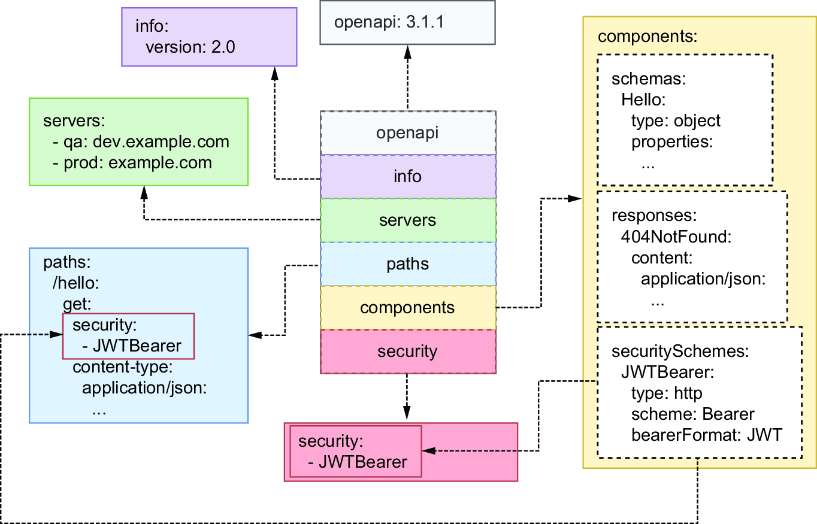
Shows how security schemes are defined in components.securitySchemes and applied globally or per operation. section 8.1


