A security zone is a logical network segment whose traffic to and from other zones is governed by distinct security policies. Firewalls use zones such as Inside, Outside, and DMZ to determine how traffic may flow. section 11.5.1 section 11.6
Stateful firewalls evaluate zone traffic in context:
- Permit reply traffic when an Inside host initiates communication with an Outside host. section 11.5.1
- Block unsolicited attempts initiated from the Outside toward the Inside network. section 11.5.1
- Apply different policies between multiple zones; unlike router ACLs, stateful filtering considers each packet’s relationship to other packets. section 11.5.1 section 11.6
DMZ placement
Place internet-facing servers in a DMZ so public clients can reach them without directly exposing hosts in the Inside zone. section 11.5.1
Figure 11.10 Simple firewall rules. Hosts in the Inside zone can initiate communications with hosts in the Outside zone, but hosts in the Outside zone cannot initiate communications with hosts in the Inside zone.
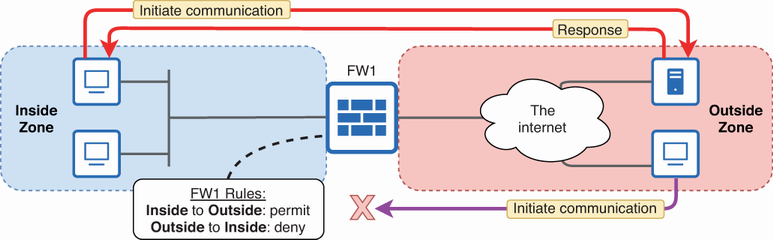
Shows the basic Inside-to-Outside initiation rule and the corresponding restriction on Outside-to-Inside initiation. section 11.5.1
Figure 11.11 Servers that need to accept connections from the internet can be placed in the DMZ without compromising the security of hosts in the Inside zone.
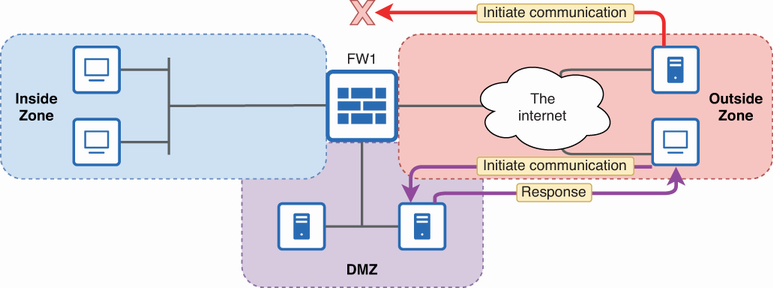
Illustrates how a DMZ separates publicly reachable servers from hosts in the Inside zone. section 11.5.1
