SecurityEvaluationContextExtension exposes security evaluation context information to SpEL expressions in Spring Data repository queries. Register it as a Spring bean, then reference the authenticated username from a query so the database retrieves only authorized records. section 12.3
Implement the data-level filtering change in two steps:
- Add a SecurityEvaluationContextExtension bean to the configuration alongside method security. section 12.3
- Add a SpEL condition such as p.owner=?#{authentication.name} to the repository query. section 12.3
- Prefer query-level selection over @PostFilter so unwanted records are not retrieved and filtered afterward. section 12.3
Owner-restricted product search
A ProductRepository query combines name matching with p.owner=?#{authentication.name}. Calling /products/c as Nikolai returns candy; calling it as Julien returns chocolate. section 12.3
Figure 12.10 In our scenario, we start by implementing the application using @PostFilter to filter products based on their owner. Then we change the implementation to add the condition directly on the query. This way, we make sure the application only gets from the source the needed records.
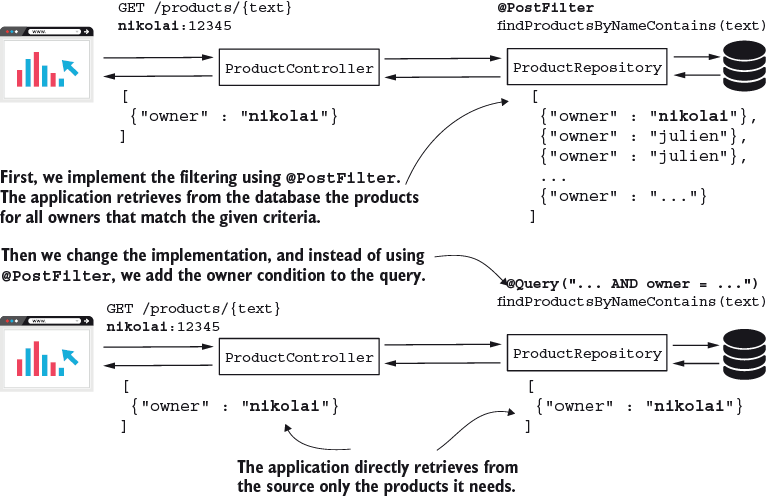
Contrasts post-selection @PostFilter with query-level selection that retrieves only the required records. section 12.3
