SELinux is a Linux labeling system that assigns labels to processes and filesystem objects, then lets the kernel enforce rules governing their interactions. Containers use it to restrict process access to designated filesystems and volumes. section 10.8 section 10.0
Container isolation uses two SELinux mechanisms:
- Type enforcement controls what processes may do according to their assigned type. section 10.8
- MCS enforcement adds categories assigned to processes, strengthening separation between container contexts. section 10.8
- SELinux works alongside namespaces, capabilities, seccomp, and read-only kernel filesystems rather than providing container isolation alone. section 1.2
Denied container access
When a container process cannot access a filesystem resource, investigate the security boundary instead of immediately using --privileged, which disables all security separation. section 10.0
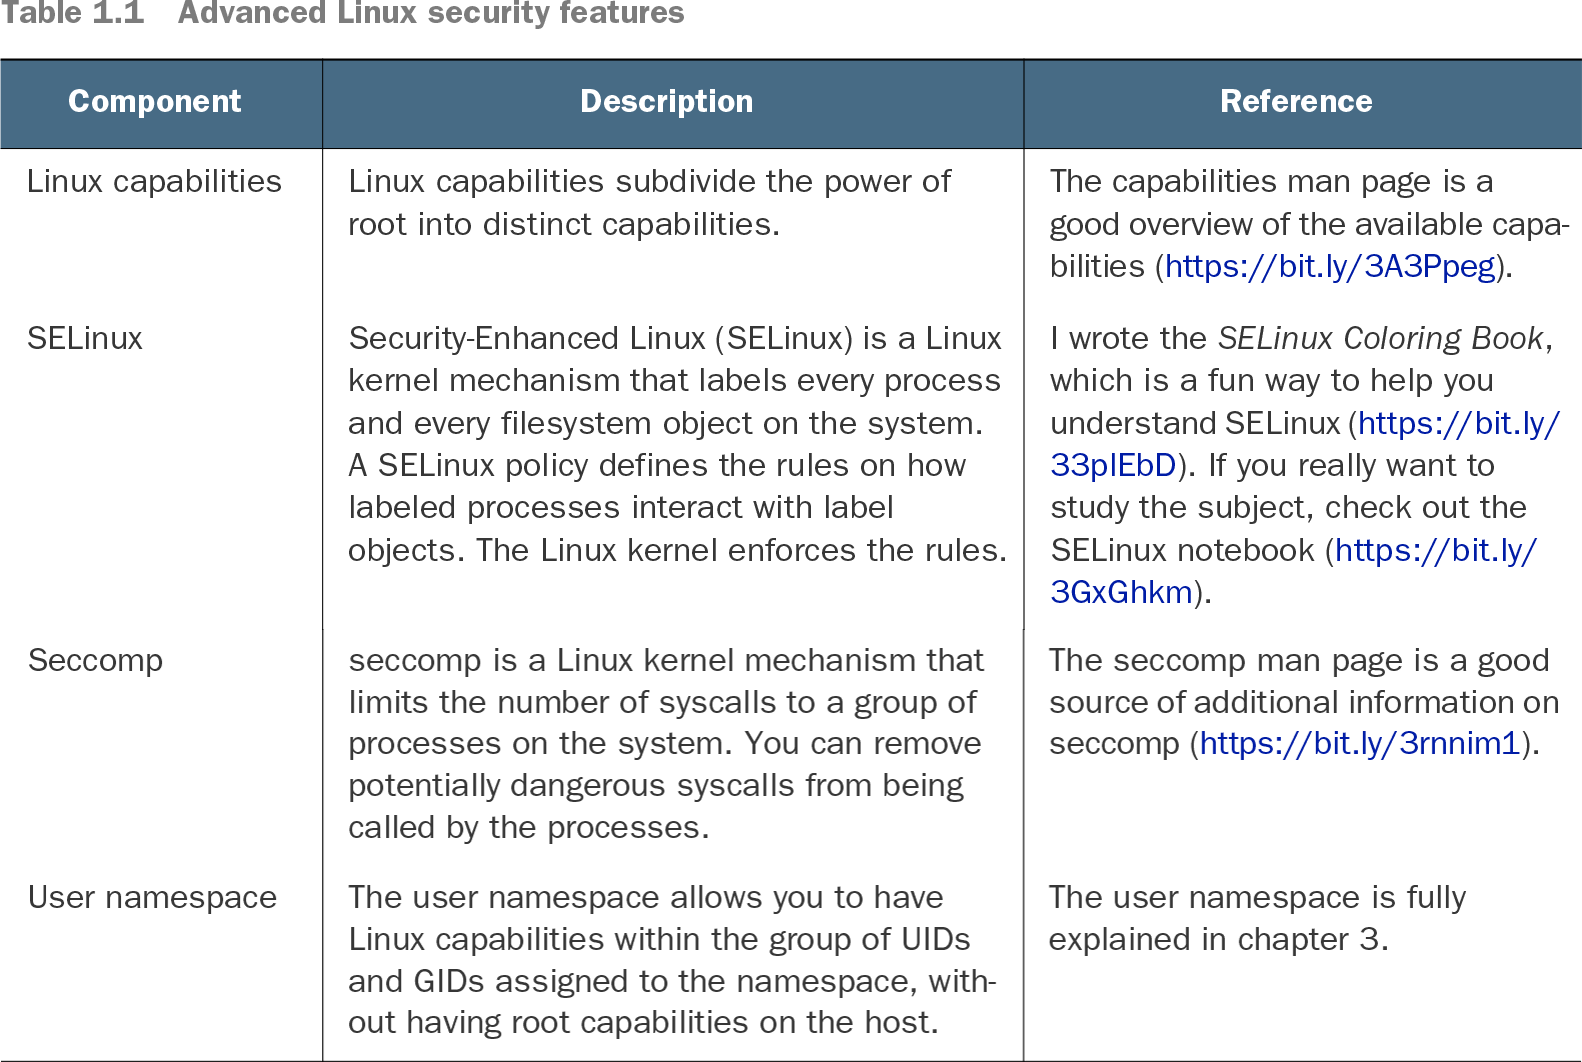
Table 1.1 Advanced Linux security features (view table figure)
| Linux capabilities subdivide the power of root into distinct capabilities. |
The capabilities man page is a good overview of the available capabilities (https://bit.ly/3A3Ppeg). |
|
| Security-Enhanced Linux (SELinux) is a Linux kernel mechanism that labels every process and every filesystem object on the system. A SELinux policy defines the rules on how labeled processes interact with label objects. The Linux kernel enforces the rules. |
I wrote the SELinux Coloring Book, which is a fun way to help you understand SELinux (https://bit.ly/33plEbD). If you really want to study the subject, check out the SELinux notebook (https://bit.ly/3GxGhkm). |
|
| seccomp is a Linux kernel mechanism that limits the number of syscalls to a group of processes on the system. You can remove potentially dangerous syscalls from being called by the processes. |
The seccomp man page is a good source of additional information on seccomp (https://bit.ly/3rnnim1). |
|
| The user namespace allows you to have Linux capabilities within the group of UIDs and GIDs assigned to the namespace, without having root capabilities on the host. |
Review SELinux alongside capabilities, seccomp, namespaces, and other advanced Linux security features. section 1.2