A ServiceAccount token authenticates workload requests to the Kubernetes API. Pods commonly use ServiceAccounts for machine-to-machine authentication, while human kubectl requests typically use client certificates or external identity providers. section 3.1
Operational points:
- Kubernetes manages ServiceAccounts as native resources associated with pods. section 3.1
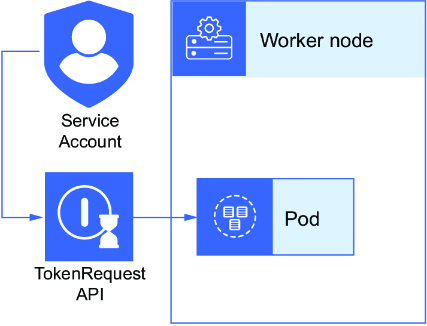
- A token is mounted into the pod through the TokenRequest API and can authenticate API requests. section 3.1
- Applications usually do not need API access, so automatic token mounting can be disabled. section 3.1
Inspect the default ServiceAccount
Run `kubectl get sa` to inspect available ServiceAccounts. A typical result includes the `default` ServiceAccount in the current namespace. section 3.1
Figure 3.2 The TokenRequest API can generate a short-lived token to authenticate to the Kubernetes API. The token expires when the pod is terminated.
The TokenRequest API generates a short-lived token for Kubernetes API authentication; the token expires when its pod is terminated. section 3.1
