A signed prekey is a medium-term public key authenticated with an identity-key signature. It lets an asynchronous X3DH exchange continue when one-time prekeys have run out. section 10.4.2
A signed prekey supports the exchange by:
- Providing authenticated public-key material through a prekey bundle. section 10.4.2
- Preserving forward secrecy up to the last signed-prekey change when one-time prekeys are depleted. section 10.4.2
- Requiring periodic rotation, such as weekly replacement, with the new public key and signature uploaded. section 10.4.2
Figure 10.12 Building on figure 10.10, to send a message to Bob, Alice fetches a prekey bundle containing Bob’s long-term key, Bob’s signed prekey, and optionally, one of Bob’s one-time prekeys. After performing different key exchanges with the different keys, all outputs are concatenated and passed into a KDF to produce an output used in a subsequent post-X3DH protocol to encrypt messages to Bob.
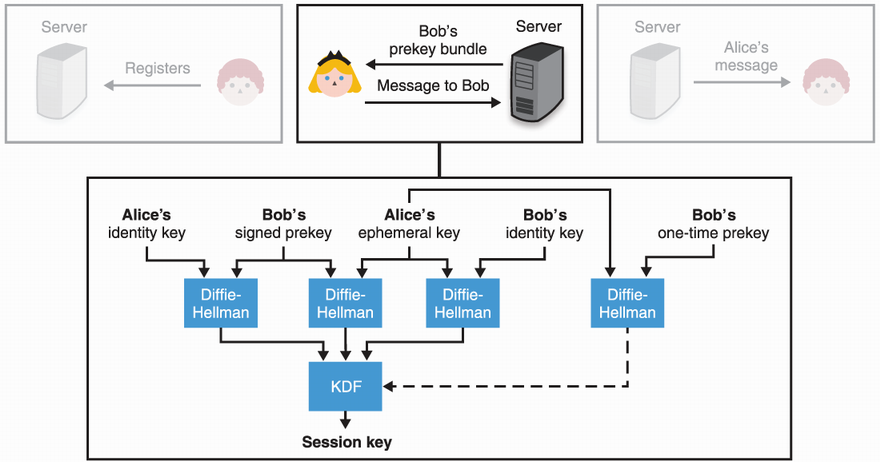
Trace how a sender fetches a prekey bundle containing the signed prekey, performs key exchanges, and derives material for message encryption. section 10.4.2
