A software bill of materials (SBOM) is a signed inventory of the packages included in a built software image from outside its source repository. It provides provenance and a cryptographic way to verify the image and incorporated packages. section 4.3.1
A platform can make SBOM handling routine by:
- Generating an SBOM during the CI/CD build. section 4.3.1
- Attaching the signed SBOM to images stored in a content-trusted registry. section 4.3.1
- Using versioned pipeline code or starter kits so teams do not perform the process manually. section 4.3.1
Figure 4.7 Steps along the way, from code creation to deployment, can automatically create the necessary provenance.
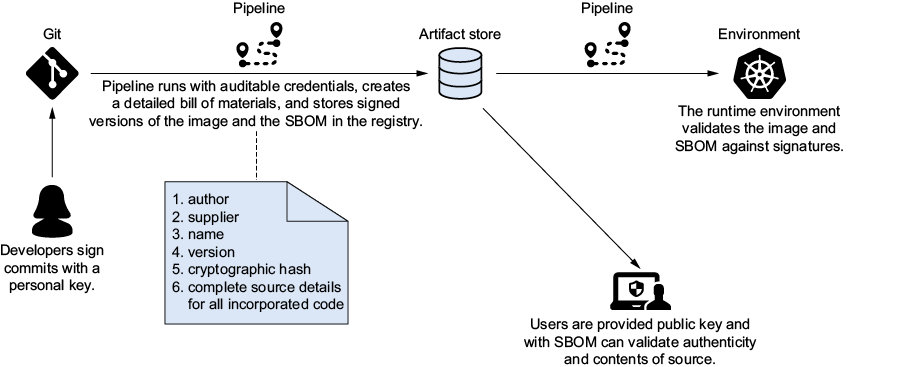
Trace how automated delivery steps create provenance from code creation through deployment. section 4.3.1

