Imagine trusting a software update because it comes from a familiar supplier. If an attacker has compromised that supplier, a dependency, or the build process, the update can carry malicious code straight into your environment. Firewalls may not stop it: the code arrives through a channel you already trust. section 11.7.1
Three incidents show different ways that trust can be exploited:
- SolarWinds (2020): attackers compromised the build system and inserted a backdoor into a legitimate update downloaded by thousands of customers. section 11.7.1
- XZ Utils (2024): an attacker gained maintainer access to an open-source library and inserted a backdoor that could have compromised SSH connections. section 11.7.1
- event-stream (2018): an attacker put malicious code into a widely used NPM package, targeting a single company. section 11.7.1
Figure 11.9 A system is only as secure as its least-secure integration.
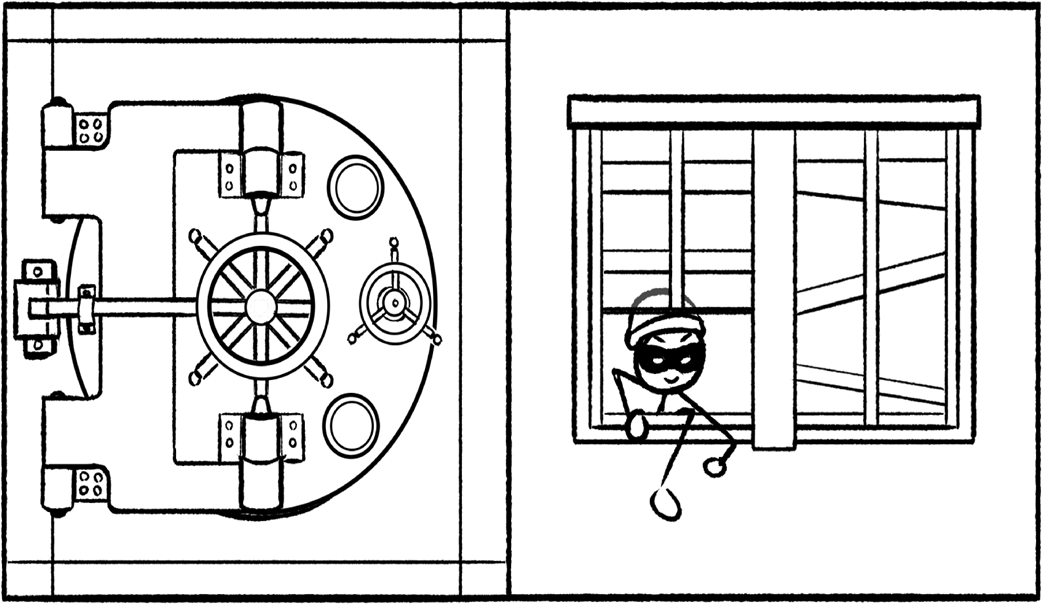
Use the figure to consider how one weak integration can undermine the security of the wider system. section 11.7.1


