spring-boot-starter-security is a Spring Boot dependency bundle that adds Spring Security to a web application. Adding it activates default security configuration, including authentication and authorization for endpoints. section 2.1
A minimal secured application demonstrates the default behavior:
- Combine spring-boot-starter-security with spring-boot-starter-web in Maven or Gradle. section 2.1
- Expose a REST endpoint such as GET /hello. section 2.1
- Call the endpoint without credentials and receive HTTP 401 Unauthorized. section 2.1
- Authenticate with the default user and generated password to receive the response body. section 2.1
Securing a Hello endpoint
With the dependency installed, GET /hello requires HTTP Basic credentials. curl -u user:<generated-password> http://localhost:8080/hello returns Hello!, while an unauthenticated request returns 401. section 2.1
Figure 2.1 Our initial application employs HTTP Basic for user authentication and authorization when accessing an endpoint. It offers a REST endpoint at a specified route (/hello). Upon a successful request, it issues an HTTP 200 status message along with a response body. This instance illustrates the default authentication and authorization mechanisms set up by Spring Security.
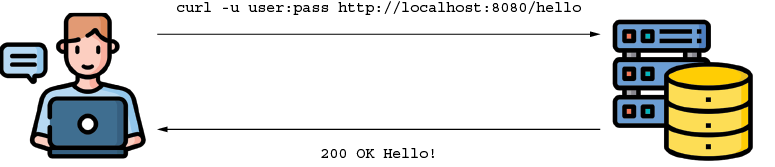
Trace the initial application flow from HTTP Basic authentication to an authorized /hello response. section 2.1
