A stateless firewall evaluates every packet independently and permits or denies it without retaining connection state or considering whether it replies to earlier traffic. Router interface ACLs are a common example. section 11.5.1
Distinguish stateless filtering from stateful filtering by examining packet context:
- Apply rules to packet attributes such as source and destination addresses or ports, without using relationships between packets. section 11.5.1
- Do not automatically allow reply traffic merely because an internal host initiated the connection; that behavior requires a stateful firewall. section 11.5.1 section 11.6
- Use router ACLs for stateless filtering, while stateful firewalls apply policies between zones such as Inside, Outside, and DMZ. section 11.5.1 section 11.6
Figure 11.10 Simple firewall rules. Hosts in the Inside zone can initiate communications with hosts in the Outside zone, but hosts in the Outside zone cannot initiate communications with hosts in the Inside zone.
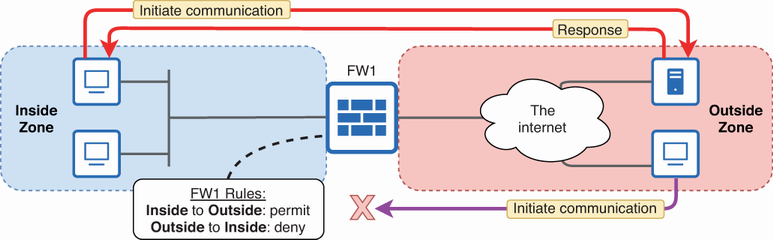
Compare the permitted Inside-to-Outside initiation with the blocked Outside-to-Inside initiation to see why stateful context matters. section 11.5.1
