SunJCE is a Java security provider: it supplies implementations behind the standard JCA and JCE APIs. Application code calls those APIs, while the installed provider performs the cryptographic operation. section 4.3
Keep these practical boundaries in mind:
- Treat provider choice as separate from application code; the standard API can route requests to different implementations. section 4.3
- Expect Java 8 and earlier SunJCE configurations to involve export-era strength limits; Java 9 and later ship with unlimited-strength encryption. section 4.3
- Compare alternatives when algorithm coverage or deployment requirements differ: Bouncy Castle and hardware-security-module providers are named alternatives. section 4.3
Hashing a file through the standard API
A Java application can request MessageDigest.getInstance("SHA3-256") and hash refunds.json without directly binding its code to a provider implementation. The resulting digest is formatted as hexadecimal. section 4.3
Figure 4.6 Application code calls the standard JCA and JCE APIs, making the code independent of the crypto algorithm implementation. The JCA and JCE layer routes calls to a provider’s implementation. Java 11-based OpenJDK ships with 13 providers out of the box.
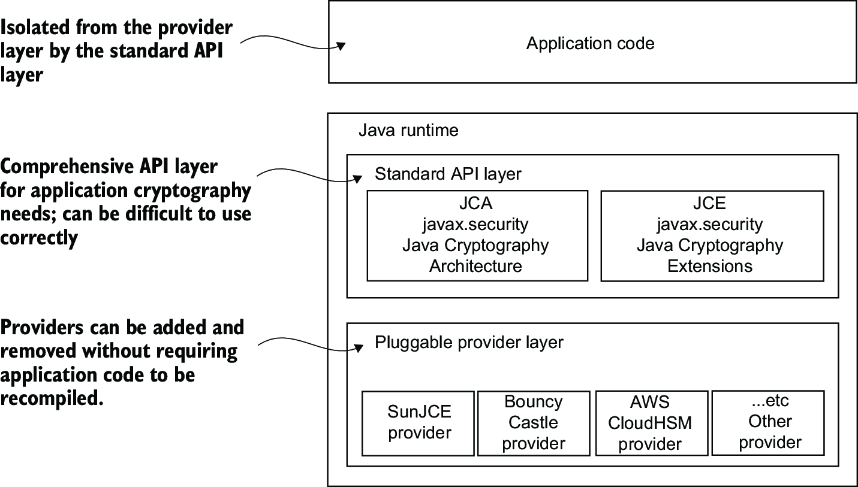
Trace how application calls pass through the JCA and JCE layers to a provider implementation. section 4.3
