A system call is an interface through which a user-space process requests services from the operating system kernel. Calls can create processes, manipulate files and devices, or establish communication channels. section 2.3.4
Applications in containers and virtual machines use system calls differently. A virtual-machine application calls its guest kernel, while containers call the single kernel running in the host operating system. section 2.1.1
System calls matter to container security because:
- Some calls are generally safe, while others require elevated privileges. section 2.3.4
- An unrestricted process could change the system clock, modify kernel memory, add or remove kernel modules, or otherwise affect neighboring containers. section 2.3.4
- Running containers without elevated privileges reduces the risk when applications do not need privileged operations. section 2.3.4
A shared-kernel risk
Imagine several containers on one Kubernetes node. Namespaces and cgroups give each container separate environments and resource limits, but a rogue program could still use a dangerous system call against the shared kernel, such as changing the system clock. section 2.3.4
Figure 2.3 The difference between running applications on bare metal, in VMs, and in containers
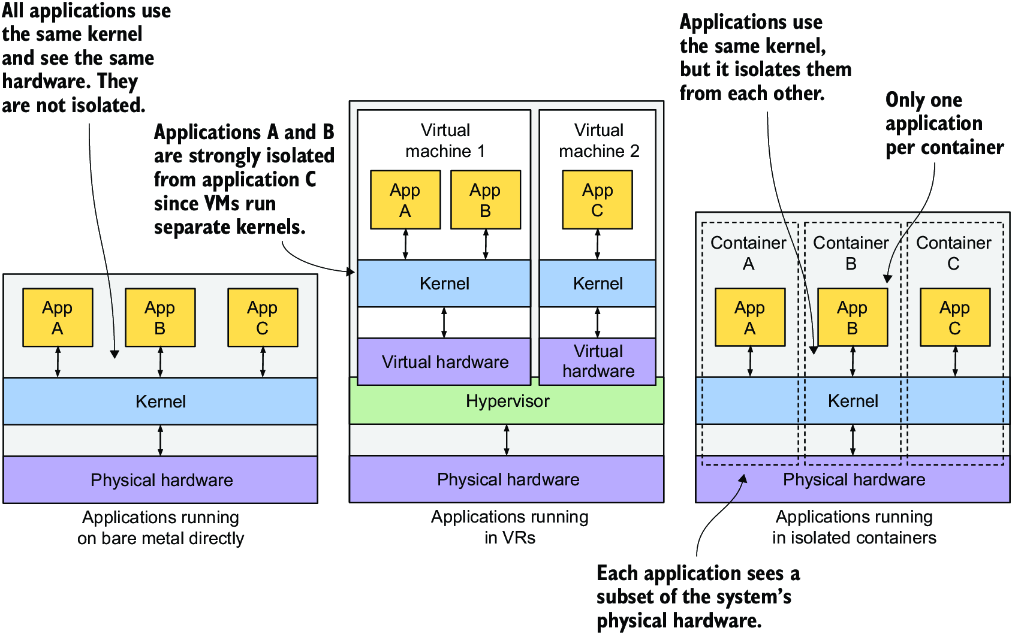
Compare applications running on bare metal, in virtual machines, and in containers to see how kernel sharing changes the isolation boundary. section 2.1.1
