TACACS+ is an AAA protocol for centralized administrative access. It separates authentication, authorization, and accounting, allowing more granular control of device users and their activities. section 11.4.2
Key implementation facts:
- Uses TCP port 49 for all client-server messages. section 11.4.2
- Encrypts the contents of all messages between the client and server. section 11.4.2
- Typically supports device administration, whereas RADIUS is typically used for network access. section 11.4.2 section 11.6
- Works with Cisco network devices and Cisco Identity Services Engine, while remaining an open standard originally developed by Cisco. section 11.4.2
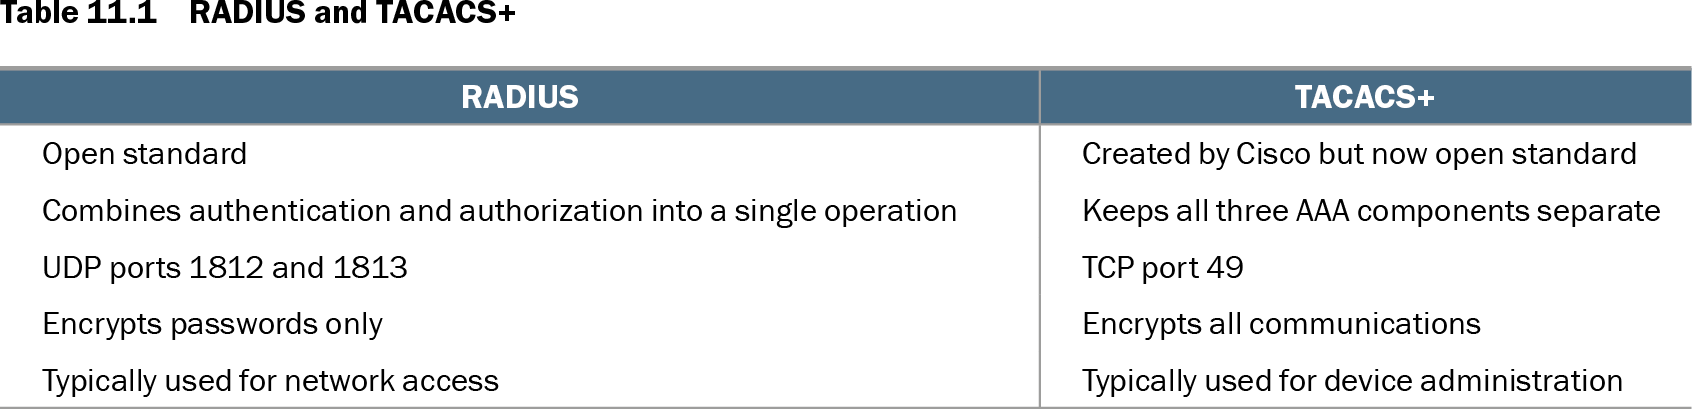
Table 11.1 RADIUS and TACACS+ (view table figure)
| RADIUS |
TACACS+ |
|---|---|
| Open standard |
Created by Cisco but now open standard |
| Combines authentication and authorization into a single operation |
Keeps all three AAA components separate |
| UDP ports 1812 and 1813 |
TCP port 49 |
| Encrypts passwords only |
Encrypts all communications |
| Typically used for network access |
Typically used for device administration |
Compare TACACS+ and RADIUS by AAA separation, transport ports, encryption scope, and typical use. section 11.4.2