Trust bootstrapping establishes authenticated access between an application and a credential service before the application has the secret needed to use that service. The application must solve three linked problems: obtaining the initial secret, storing it safely, and changing it without interrupting access. section 2.2
Treat bootstrapping as a platform responsibility rather than an application-specific shortcut. Centralize passwords, API keys, certificates, and other runtime secrets in a credential store, while recognizing that credential services commonly expose proprietary APIs rather than one industry-standard interface. section 2.2
Figure 2.9 A credential management service and an SSO service are two foundational components of cloud-native application security. As a developer, you can use the OIDC and WebAuthn protocols to interact with all modern SSO services. But for credential services, there is no industry-standard API, so you have to use a proprietary API provided by the credential service’s implementation.
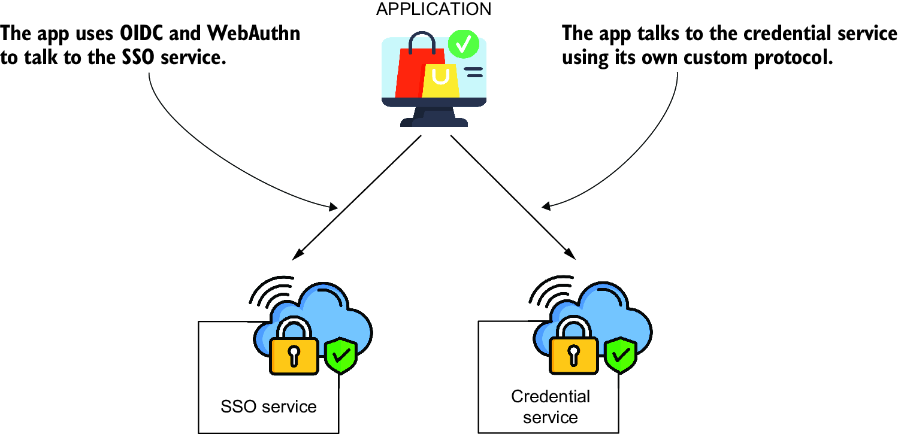
Use the security-service relationship diagram to distinguish standardized SSO integrations from proprietary credential-service access. section 2.2
