Two-key credential rotation keeps a service account’s previous credential valid while a replacement becomes available. This prevents an in-progress pipeline from failing when the credential in the secrets store changes. section 6.4.4
For an automated rotation:
- Maintain two valid keys, but put only the latest credential in the secrets store for newly launched jobs to fetch. section 6.4.4
- Keep the prior key valid until the next rotation so jobs already using it can finish. section 6.4.4
- Choose the interval with both keys in mind: rotating every seven days keeps the active key at most seven days old and rotates both keys within fourteen days. section 6.4.4
Figure 6.19 Our service account has two valid credentials at any given time. Only the latest credential is maintained in the secrets store, and the prior keys remain valid until the next rotation to prevent workloads and orchestration from failing due to the race condition of the key being changed while a job is already in process.
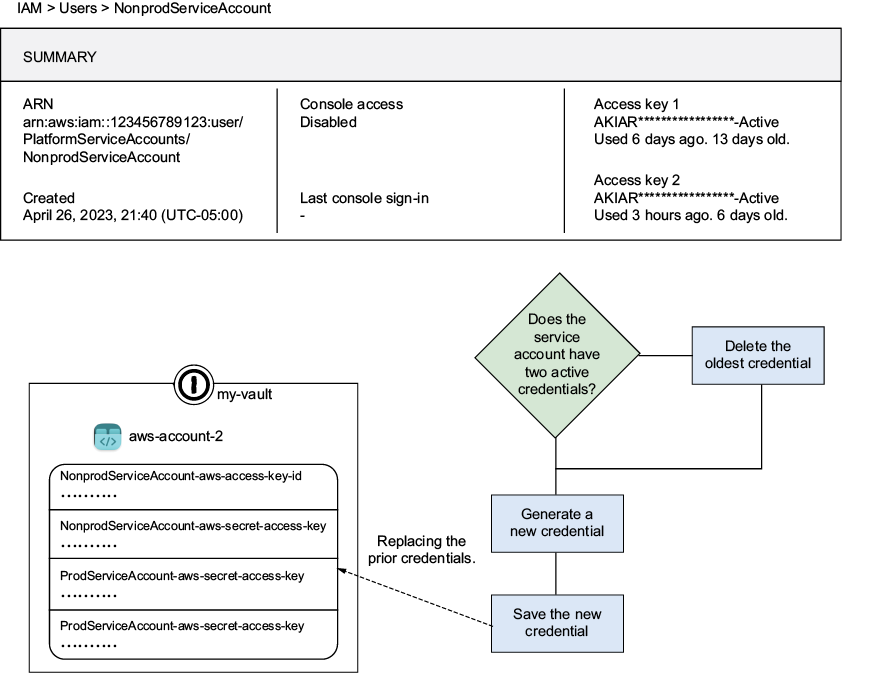
The diagram shows why the secrets store holds the newest credential while the previous key remains usable by work already in progress. section 6.4.4
