A validating webhook is an HTTP callback used by a Kubernetes admission controller to inspect a requested deployment operation and accept or reject it before the change proceeds. section 4.1.1
Use it to separate compliance work from compliance verification. Rather than rescanning an image, the webhook can compare its commit SHA with an authoritative vulnerability-scan record. It can also enforce required deployment labels directly. section 4.1.1
Deployment admission check
A reusable pipeline performs the vulnerability scan, while a validating webhook blocks deployment when the image lacks a successful scan record or the deployment omits required labels. Gatekeeper can provide the admission-control implementation. section 4.1.1
Figure 4.3 Kubernetes admission controller
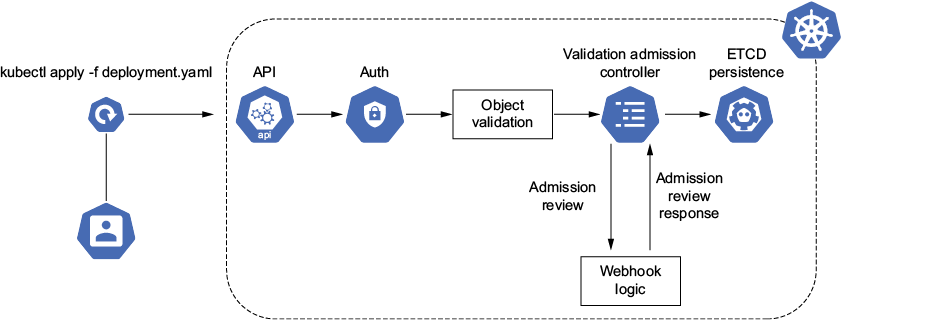
Inspect the Kubernetes admission-controller flow that intercepts deployments for verification. section 4.1.1
Figure 4.4 Admission controller built using Gatekeeper (https://github.com/open-policy-agent/gatekeeper), which checks for labels on the deployment
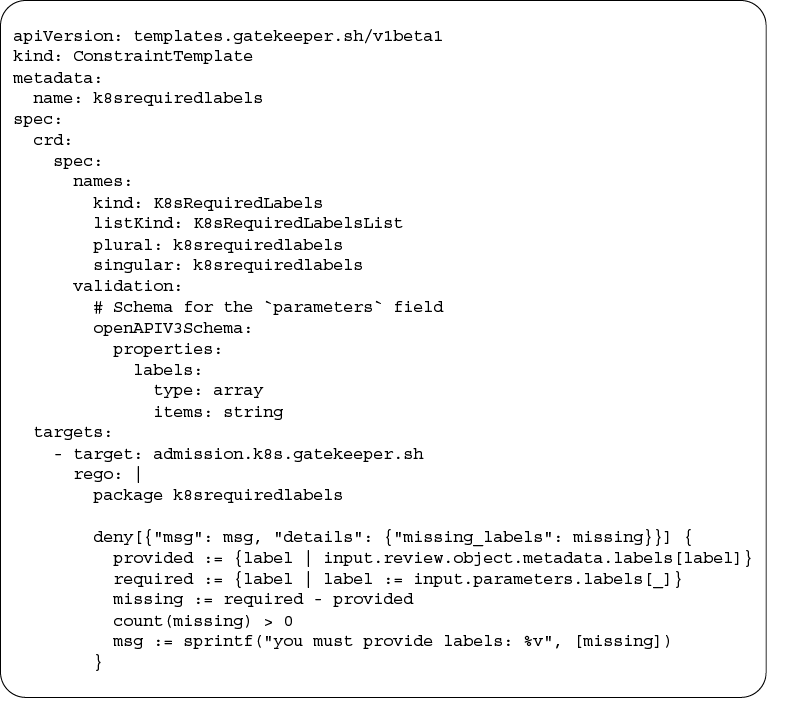
Inspect a Gatekeeper-based admission controller enforcing deployment labels. section 4.1.1
