A volumetric denial-of-service attack overwhelms a service with millions of network requests or packets, consuming resources until legitimate users cannot receive responses. It may target the application layer, but more commonly targets layers 3–6 of the OSI model. section 9.3
Common forms include:
- ICMP, or ping, floods send packets without waiting for replies, consuming server resources. section 9.3
- SYN and UDP floods, DNS and UDP amplification attacks, and IP fragmentation attacks overwhelm network services in different ways. section 9.3
- Application-layer flooding can send millions of HTTP requests; unrestricted resource retrieval, such as requesting millions of products, creates a related failure mode. section 9.3
Figure 9.14 A common DoS attack is ping flood. The goal of this attack is to overwhelm the server with an unlimited number of ping requests until it can no longer respond to requests from legitimate users.
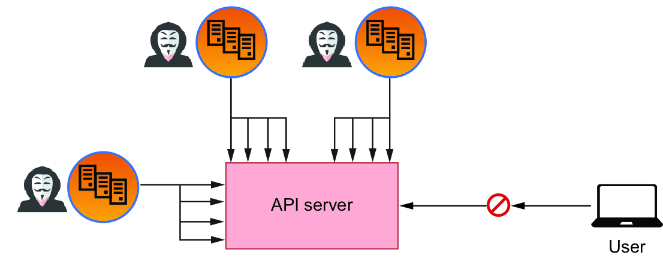
Use the ping-flood illustration to visualize how unlimited requests can prevent legitimate users from receiving responses. section 9.3
