An approver is the person who confirms that an authorization policy expresses the intended business rule and has the right scope before it progresses through governance. The approver may also be the policy owner, but remains distinct from the author and reviewer when separation of duties applies. section 14.3.2 section 14.3.1
The approver participates in a policy life cycle alongside related governance roles:
- Confirms business intent and policy scope rather than performing the implementation review. section 14.3.2
- Follows authoring and review before approval, while the reviewer evaluates the implementation and must differ from the author. section 14.3.2
- Operates within shared templates, metadata, review processes, and deployment controls that preserve consistency without centralizing every decision. section 14.3.1
- Retains accountability for an approval record as incidents, audit findings, monitoring results, and review cycles generate policy updates. section 14.6
Approval in a policy workflow
Alice authors an authorization policy and records its rationale. Bob reviews the implementation. Carol approves the policy’s intent and scope. Renee checks alignment with shared authorization standards, while Arnold later verifies review timing, metadata, and follow-up actions. section 14.3.2
Figure 14.5 Policy governance workflow across roles. Authorization policies move through clearly defined roles, from creation to deployment and review. Engineers author and review policy logic, managers approve intent and scope, access control coordinators ensure alignment across teams, and auditors verify that governance processes are followed over time. Separation of duties and feedback loops preserve accountability without centralizing control.
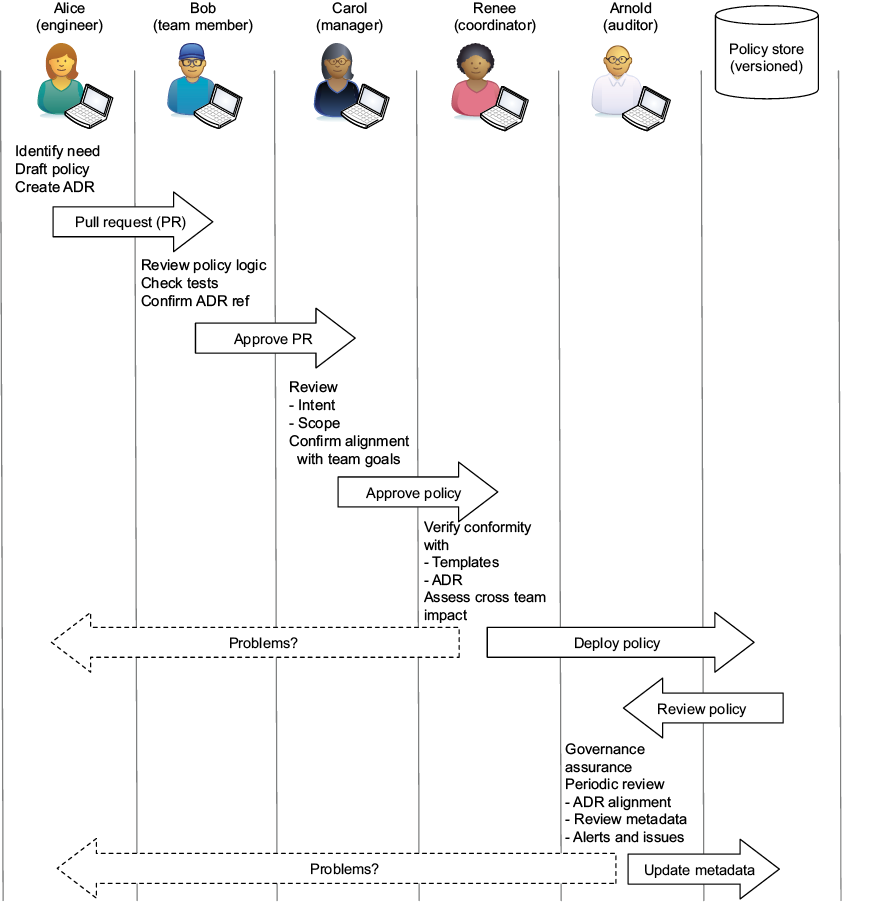
Trace how approval connects policy creation, implementation review, coordination, deployment, and ongoing audit. section 14.3.2

