Broken function-level authorization (BFLA) occurs when an API lets a user invoke an operation outside that user’s role. A normal user reaching an admin endpoint is performing vertical privilege escalation; accessing another user’s data is the separate problem of BOLA. section 4.7
An unprotected admin endpoint
An endpoint such as GET /admin is vulnerable when it returns success without checking the caller’s role. To mitigate it, validate the access token, read its permissions claim, and allow the operation only when it contains admin. Return 403 when credentials are valid but insufficient; use 404 instead when concealing a sensitive endpoint is preferable. section 4.8
Apply these checks to reduce BFLA risk:
- Declare roles or permissions explicitly in access tokens. section 4.11
- Evaluate the caller’s permissions for every requested operation, including admin and developer APIs hidden behind subdomains or URL paths. section 4.7
- Test endpoints as users with different roles, rather than treating undisclosed paths as protected. section 4.7
Figure 4.15 A good strategy to prevent BFLA is to declare user roles explicitly in access tokens and check those roles on every request across all operations.
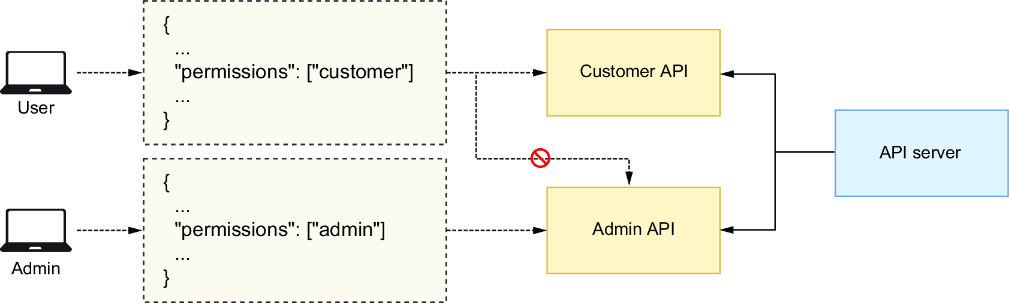
Use the role-check flow as a mental model: declare roles in access tokens, then check them on every operation. section 4.7
