A claim is an assertion about an authenticated user, such as the teams they belong to. Platform services can use claims returned with identity data to determine which team resources a user may access. The identity provider (IDP) should convey this authorization data, not become its source of truth. section 4.3.3 section 7.3.2
Team membership may be self-managed in a system such as GitHub. Configure the IDP to retrieve that information after login and include it in a verifiable JSON Web Token (JWT). Prefer an automated OpenID Connect integration over a tool that requires tickets and manual role assignment: the latter turns routine access into developer friction. section 4.3.3 section 7.3.2
Team access from a CLI
A developer starts a device-authorization flow in a platform CLI and authenticates through GitHub in a browser. The IDP uses the resulting access token to request the developer’s organization teams, then creates a verifiable JWT whose ID token contains the team list as a claim. The CLI can use that result to give the developer access to their team’s platform resources. Auth0 is one option for providing the IDP service; its configuration can be automated rather than maintained by hand. section 7.3.2
Figure 7.9 In this authentication and authorization flow, the IDP acts just as a secure go-between. The user must authenticate through GitHub and grant their device authorization to receive a JSON Web Token.
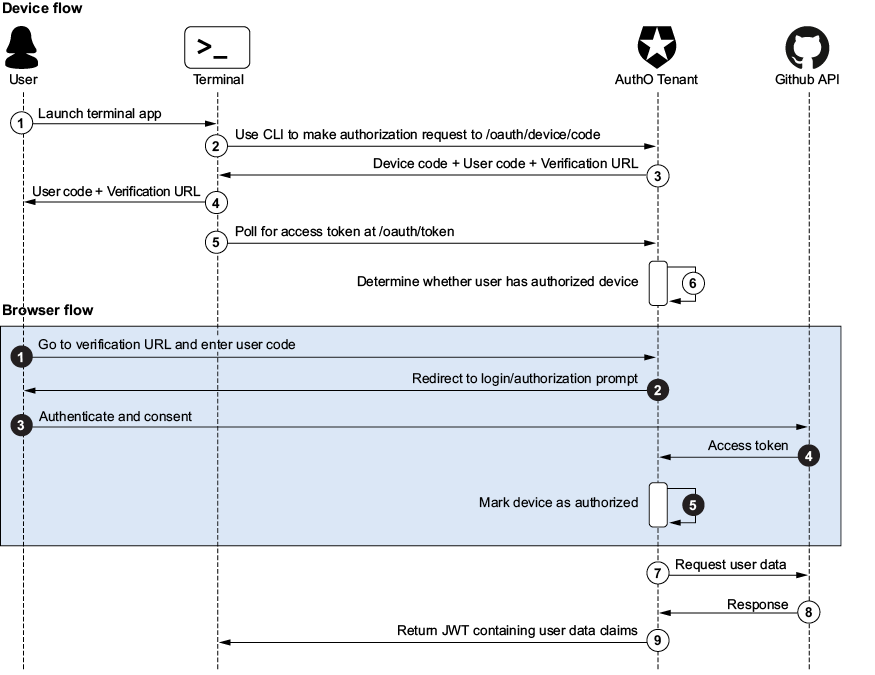
The flow shows the IDP acting as a go-between: GitHub handles user authentication and device authorization before the user receives a JWT. section 7.3.2






