A policy engine evaluates requests against configured rules and decides whether they may proceed. With the ACM Policy Controller enabled, a ValidatingWebHook registers Gatekeeper as a Kubernetes admission controller. The API server sends object requests to Gatekeeper before admitting them. section 13.4.1
For a Pod creation request, Gatekeeper checks the configured policies for violations. A denial prevents the API server from creating the Pod and returns the policy error. Policies use constraint templates and constraints; a constraint can match Pod objects and specify dry-run enforcement. section 13.4.1
Evaluation typically takes about one millisecond, but a poorly performing policy can add system latency. Check policy performance when introducing custom rules. section 13.4.1
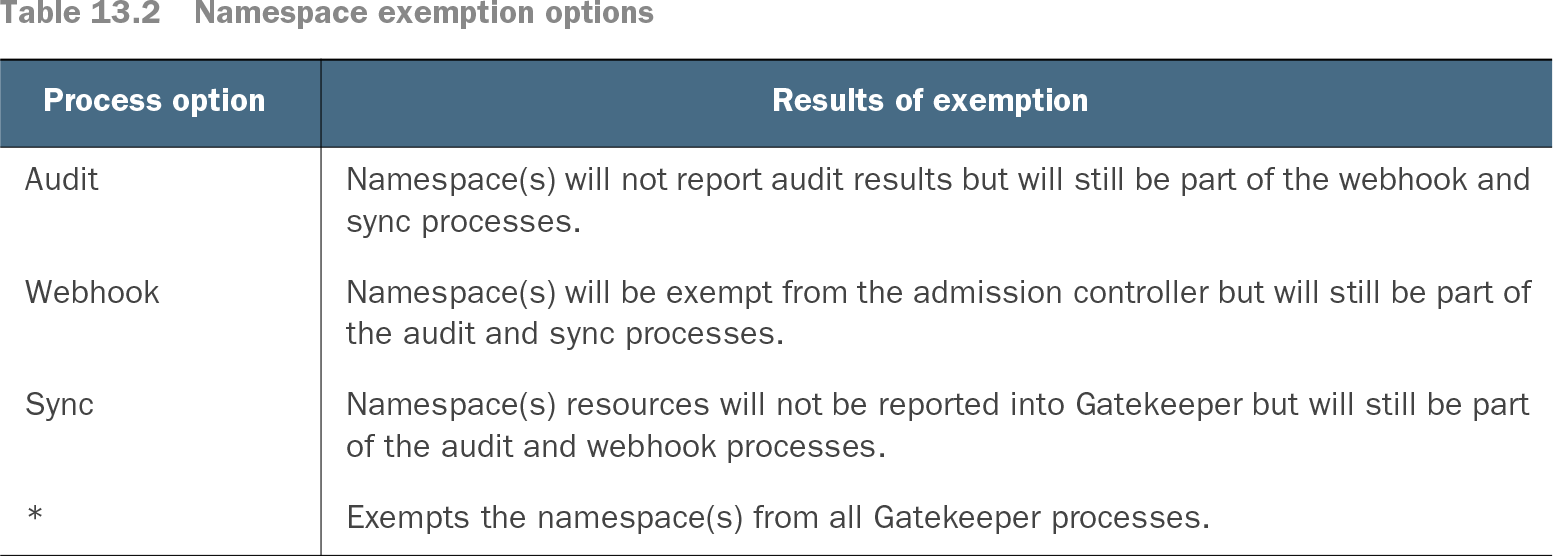
Table 13.2 Namespace exemption options (view table figure)
Namespace exemptions can apply separately to audit, webhook admission, and sync, or to all Gatekeeper processes. Choose the process deliberately: a webhook exemption does not also suppress audit results. section 13.4.1