A CODEOWNERS file assigns individuals or teams responsibility for reviewing specified files, file types, or directories. When a pull request changes an owned path, the listed owners must approve it before merging, and they are notified of the review request. section 8.9
Use the file to bring API governance into source review where API linting and breaking-change checks cannot provide policy or design judgment. Keep ownership narrowly scoped: excessive external approvals can delay delivery and increase development friction. section 8.9
A practical GitHub setup follows these steps:
- Create CODEOWNERS in the repository root; if a template is named _CODEOWNERS, rename it and add the responsible colleague’s GitHub ID. section 8.5.6
- Commit the file, open a pull request, and merge it into the main branch. section 8.5.6
- Add the reviewer as a repository collaborator, then configure branch protection to require code-owner approval, pull requests, and passing build and API-review status checks. section 8.5.6
- Test the control by changing documentation in the owned directory and verifying that the pull request requires the code-owner review. section 8.5.6
API governance ownership
Assign the API governance team as code owners for API definition files, while leaving routine changes to the team maintaining the repository. A single reviewer can be replaced by a team where the hosting platform supports team ownership. section 8.9 section 8.5.6
Figure 8.7 Setting up GitHub branch protection rules
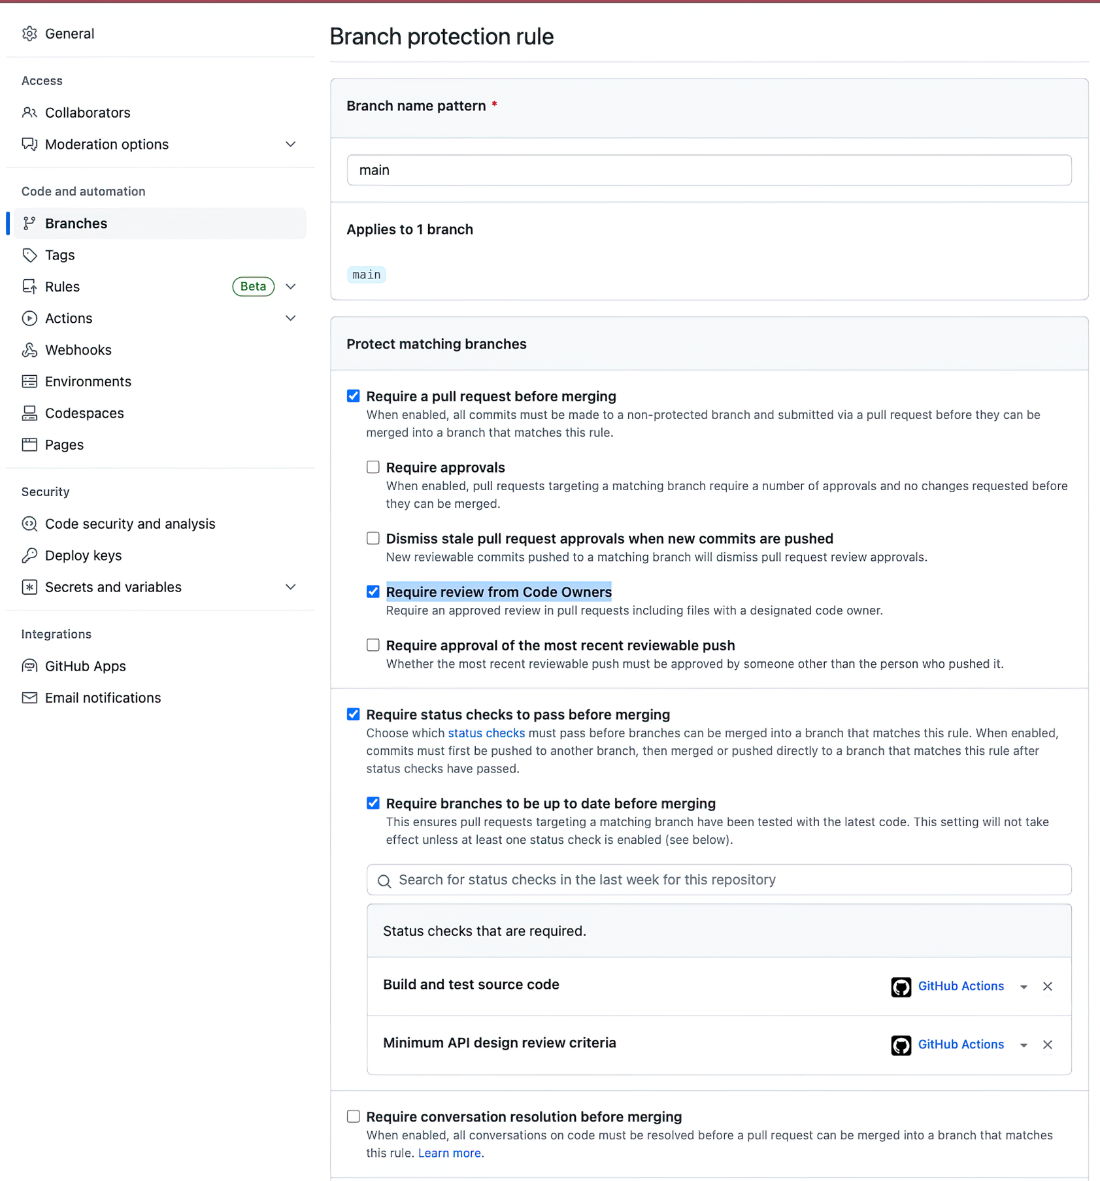
Use the branch-protection configuration view to verify that code-owner reviews and the selected build and API-review status checks are mandatory before merging. section 8.5.6

