liveBook · Manning

Branch protection

As explained in GitHub Actions in Action: Continuous integration and delivery for DevOps

A branch protection rule is a repository rule that controls which changes and operations are permitted for a branch.

Branch protection is a repository control that restricts how changes reach selected branches. It supports traceability, mandatory review, segregation of duties, and standardized CI/CD practices. section 11.1.1 section 11.4

Configure branch protection to enforce controls such as:

  • Require signed commits so GitHub rejects pushes containing unverified commits. section 11.1.1
  • Require pull requests and approvals before changes merge into the main branch. section 11.2
  • Prevent administrators from bypassing the rule; changes to protection settings remain visible in audit logs. section 11.2
  • Add CODEOWNERS when review responsibility must be separated among designated owners. section 11.2

Signed-commit workflow

Generate a GPG key, configure Git with user.signingkey, enable commit.gpgsign, and create signed commits with git commit -S -m "Your commit message". When an unverified commit is pushed, the protected branch blocks it. section 11.1.1

Figure 11.4 Branch protection rules
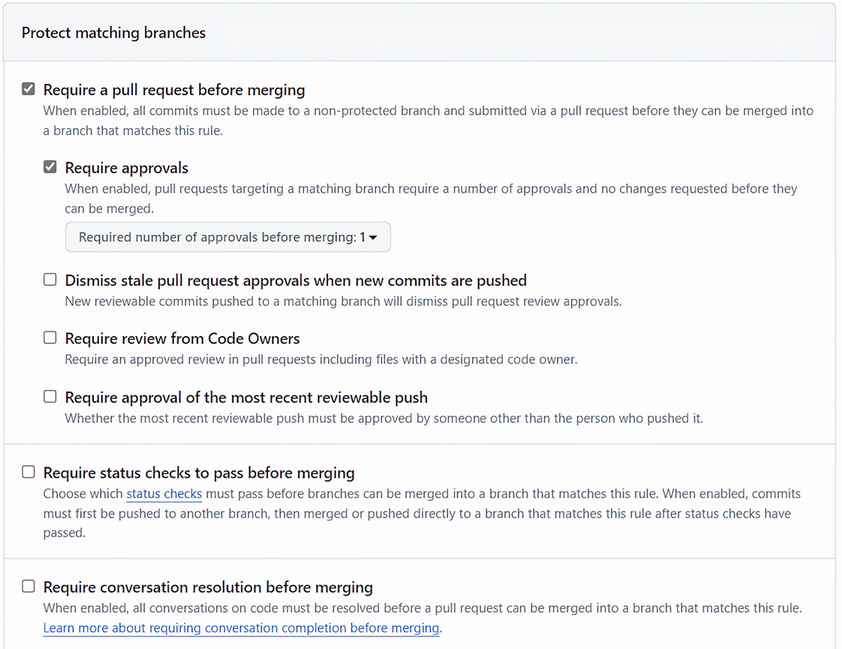
Use the branch-protection configuration view to locate pull-request, approval, and administrator-bypass controls. section 11.2

How GitHub Actions in Action: Continuous integration and delivery for DevOps covers it

How deep it goes
Explains signed-commit and review settings with configuration steps, but defers broader branch-rule options and detailed CODEOWNERS mechanics.
Examples
Uses GPG-signed commits, rejected unverified pushes, required pull-request approvals, administrator bypass controls, and CODEOWNERS.
What it assumes
Assumes Git and repository administration, while teaching signed-commit configuration and the rationale for peer review from the controls upward.
What you can do after
Operate GitHub repository controls that require signed commits, enforce reviewed merges, and preserve auditable protection changes.
How it connects
Connects branch protection with signed commits, pull requests, code review, CODEOWNERS, audit logs, single sign-on, and GitHub Actions environments.

Related concepts

This explainer was generated by Manning's knowledge graph from the text of GitHub Actions in Action: Continuous integration and delivery for DevOps. The section links point to the parts of the book it draws on.