Credential management protects the credentials and access tokens that establish user identity and permissions. Weak passwords, repeated credentials, or exposed tokens can let attackers take over accounts and undermine API security. section 4.4
Reduce common credential-management failures by:
- Enforcing stronger password policies and preventing repeated brute-force attempts. section 4.4
- Defending against credential stuffing when users reuse credentials leaked from other websites. section 4.4
- Keeping passwords and access tokens out of URLs, and requiring password confirmation before changing sensitive account details. section 4.4
- Treating multistep login flows as an enumeration risk unless threat detection prevents account discovery. section 4.4
Figure 4.3 An authentication system manages users’ identities, credentials, and access permissions. When a user logs in, they get back an API access token with specific permissions.
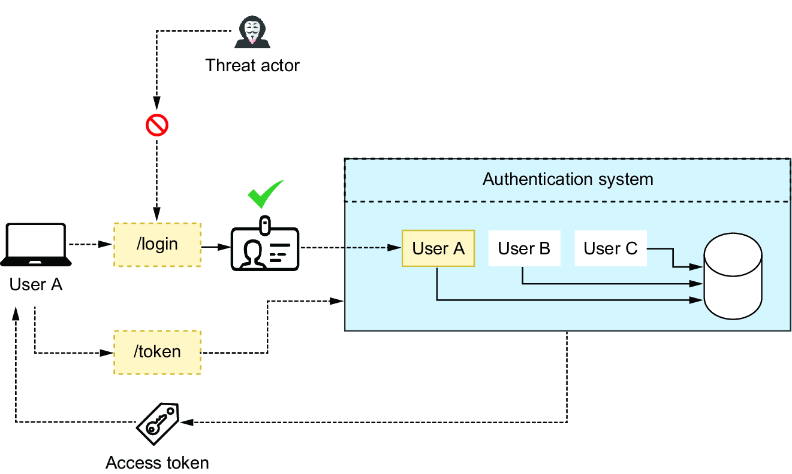
Use the authentication-system diagram to connect identities and credentials with issued API access tokens and permissions. section 4.4
Figure 4.4 Credential stuffing is a common exploit in which threat actors use leaked user credentials from other websites and insert (stuff) them into our API to try to take over other user accounts.
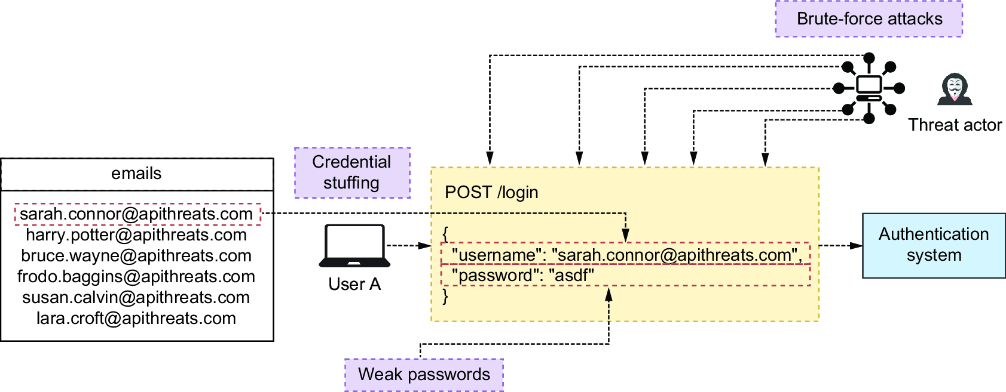
Use the credential-stuffing figure to visualize how leaked credentials from another website can drive account takeover. section 4.4
