Credential stuffing is an attack that reuses leaked username-and-password pairs from one website against another service to take over accounts. It succeeds because users often reuse credentials across multiple websites. section 4.4
A reused password becomes an API attack
Suppose credentials leak from one website. An attacker inserts those username-and-password pairs into another website’s API, trying multiple logins until a reused combination grants access to someone else’s account. section 4.4
Useful defensive checks include:
- Check whether login defenses prevent repeated username-and-password attempts; unrestricted attempts enable brute-force attacks. section 4.4
- Treat credential management as part of the wider authentication and authorization strategy, because account takeover can undermine both. section 4.4
Figure 4.4 Credential stuffing is a common exploit in which threat actors use leaked user credentials from other websites and insert (stuff) them into our API to try to take over other user accounts.
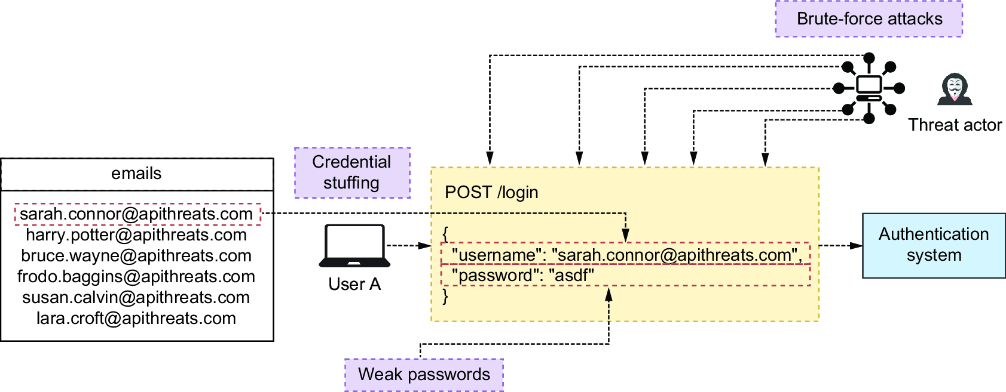
Illustrates leaked credentials from other websites being inserted into an API to attempt account takeover. section 4.4


