Data in use is information actively processed in computer memory. Unlike data in transit or data at rest, it cannot be protected by ordinary transmission or storage encryption while computation is happening. section 9.2.1
During processing, computers typically load data into RAM in clear text. Anyone able to inspect memory—including a malicious actor or cloud provider—could read or copy it. section 9.2.1
Confidential computing addresses this exposure by:
- Running sensitive computation inside a trusted execution environment, also called an enclave. section 9.2.1
- Using CPU extensions to encrypt memory access while data remains in use. section 9.2.1
- Supporting secure multiparty collaboration, such as training an AI model on sensitive hospital data. section 9.2.1
Figure 9.2 The three states of data: at rest, in transit, and in use. Each state represents a potential point of vulnerability where data can be exposed or compromised if not properly protected.
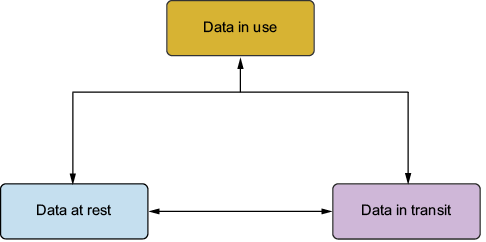
Compare data at rest, data in transit, and data in use as three points where information may be exposed. section 9.2.1
