Defense in depth combines multiple security layers to reduce the likelihood of a successful breach. Each layer makes an attack harder and provides protection if another control fails. section 1.8
Apply the strategy across the security journey:
- Secure workloads with more than one security control and more than one Azure security service. section 1.8
- Monitor and detect threats as additional layers of protection. section 1.8
- Investigate and respond when an attack progresses or a control fails. section 1.8
- Protect identities, data, applications, infrastructure, and network resources rather than relying on one control. section 1.8.3
The goalkeeper analogy
A goalkeeper is easier to bypass than a goalkeeper protected by several other players. Likewise, each additional security layer forces an attacker past another control, while remaining layers continue protecting resources when one fails. section 1.8
Figure 1.7 Azure security services that can be used to secure data and applications in your Azure environment
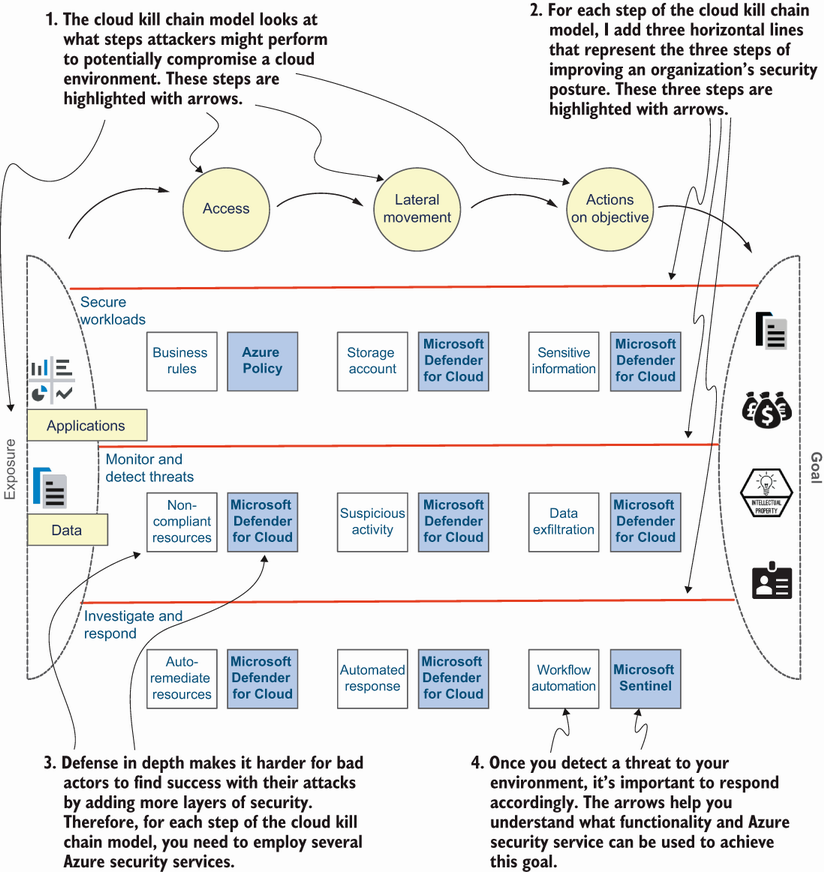
Use the security-services figure to relate layered Azure protections to threats targeting applications and data. section 1.8.3






