The EC2 metadata service is a locally reachable endpoint that provides information about an Amazon EC2 instance, including credentials associated with its IAM roles. section 5.2
SSRF against instance credentials
The endpoint http://169.254.169.254/latest/meta-data/ can reveal IAM role information and credentials. If a server-side request forgery (SSRF) flaw lets an attacker reach it, the attacker may reuse those credentials to call AWS APIs directly. section 5.2
Reduce this exposure by:
- Using IMDSv2, which requires a temporary token instead of allowing a single GET request. section 5.2
- Upgrading EC2 instances to IMDSv2; it ships by default with Amazon Linux instances since March 2023. section 5.2
Figure 5.5 Capital One’s SSRF attack happened due to a misconfiguration in its WAF, which allowed the threat actor to relay a request to Capital One’s EC2 instance metadata endpoint and retrieve its AWS access keys.
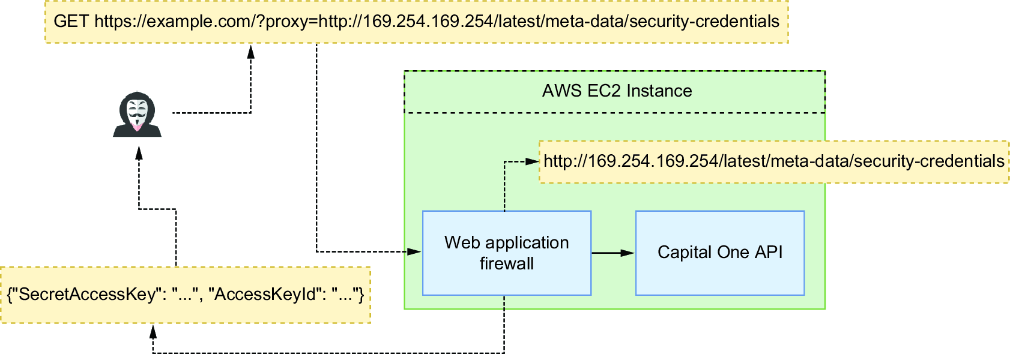
The figure illustrates how a WAF misconfiguration enabled SSRF to relay a request to the EC2 metadata endpoint and retrieve AWS access keys. section 5.2

