An egress gateway is a service-mesh perimeter proxy that controls traffic leaving an Anthos cluster or mesh for external services. It centralizes outbound routing and can support TLS origination through a dedicated gateway or an external HTTPS proxy. section 4.5.3 section 10.4.3
Configure egress control by combining these components and policies:
- Deploy the istio-egressgateway as a second proxy at the service-mesh perimeter. section 10.4.3
- Set outboundTrafficPolicy to REGISTRY_ONLY so unregistered outbound destinations are blocked. section 10.4.3
- Create ServiceEntries for approved external services, identifying them with location MESH_EXTERNAL. section 10.4.3
- Use NetworkPolicies and firewall rules instead when ASM is not deployed; Pod egress can be restricted through node IP subnets. section 10.4.3
Allowing an external HTTP service
A ServiceEntry can allow HTTP traffic to httpbin.org on port 80 while marking the destination as external:\n\napiVersion: networking.istio.io/v1alpha3\nkind: ServiceEntry\nmetadata:\n name: httpbin-ext\nspec:\n hosts:\n - httpbin.org\n ports:\n - number: 80\n name: http\n protocol: HTTP\n resolution: DNS\n location: MESH_EXTERNAL section 10.4.3
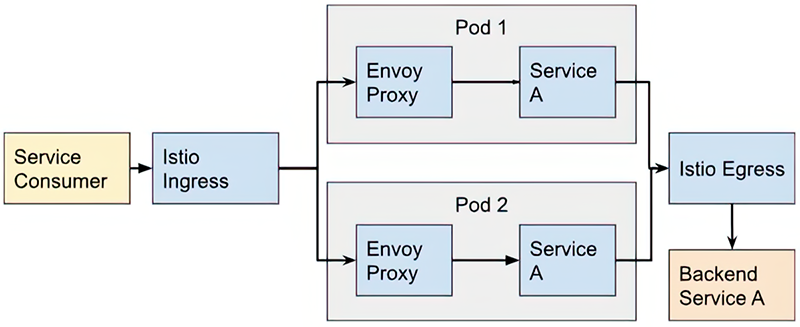
Use the egress-control architecture illustration to inspect how mesh traffic is routed toward external services. section 4.5.3
