In an elliptic-curve group, scalar multiplication repeatedly adds a point to itself. The elliptic-curve discrete logarithm problem (ECDLP) asks you to recover the scalar x when you know G and P = [x]G. section 5.3.1
The recovery challenge
Choose a point G and add it to itself x times to produce P. Computing P from G and x is scalar multiplication; recovering x from only G and P is the ECDLP. section 5.3.1
Figure 5.11 Elliptic curve cryptography (ECC), in practice, is mostly specified with elliptic curves in coordinates modulo a large prime number p. This means that what we use in cryptography looks much more like the right graph than the left graph.
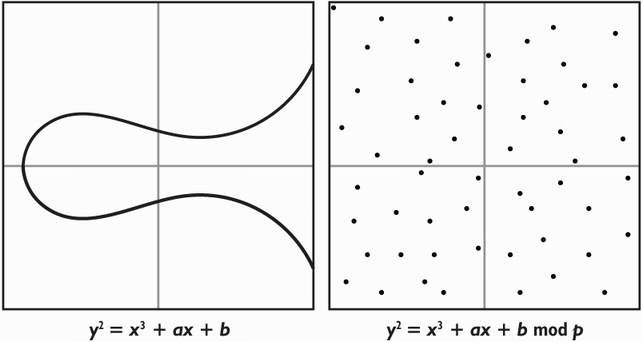
Use the coordinate view to see that practical elliptic-curve cryptography works with points modulo a large prime p. section 5.3.1


